Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Define the support operation before delegating access
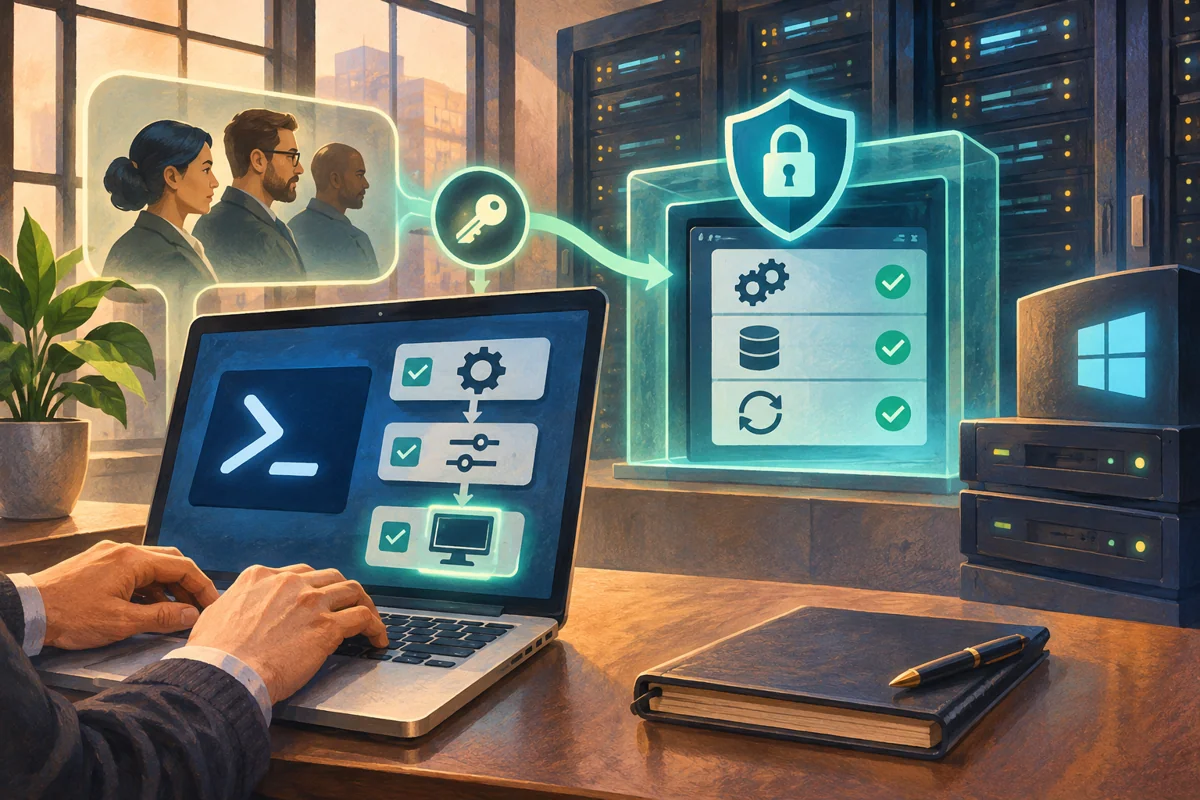
Just Enough Administration provides a PowerShell endpoint that exposes an approved command set instead of unrestricted administration. Its value comes from a carefully reviewed capability and identity model. A poorly designed endpoint that permits arbitrary code, unsafe external programs or over-broad function parameters can undermine the intended boundary even when its name includes “restricted”.
For managed Netcloud24 operations, the team can prepare a bounded support interface for agreed tasks without distributing general administrator credentials. Customers or support users receive the approved access path, not responsibility for constructing a security endpoint. This example establishes a read-only service-inspection capability on a member server. It does not delegate service restarts or apply the same virtual-account model indiscriminately to a domain controller.
Choose execution identity and an emergency route
Decide which local or network resources the endpoint needs. RunAsVirtualAccount can supply a temporary local identity for endpoint operations, while a gMSA is a different choice for suitable network requirements. By default, virtual-account privileges can be powerful, particularly on domain controllers. Keep this pilot on a member server and explicitly select a restricted local group for its run-as token.
Maintain a separate approved administrator endpoint or console path to repair configuration. The operator creating JEA needs sufficient local administrative authority, but delegated users should not be added to Administrators merely to connect. Plan transcript storage, access and retention because JEA sessions can produce sensitive operational evidence.
Keep module and role files writable only by trusted administrators. A user able to alter a role capability or a function it calls can change what the endpoint permits. JEA cannot compensate for a writable code path beneath its policy.
Create a protected role module
Place a module in the server’s recognised module path with a RoleCapabilities directory. Use a distinct role name to avoid ambiguity if several modules expose the same capability name. The example allows Get-Service for inspection; it intentionally makes no claim to limit visibility to one service.
$moduleRoot = 'C:\Program Files\WindowsPowerShell\Modules\ManagedSupportJEA'
New-Item -ItemType Directory -Path ($moduleRoot + '\RoleCapabilities') -Force | Out-Null
New-ModuleManifest -Path ($moduleRoot + '\ManagedSupportJEA.psd1') `
  -ModuleVersion '1.0.0' -Guid ([guid]::NewGuid())
New-PSRoleCapabilityFile `
  -Path ($moduleRoot + '\RoleCapabilities\ManagedServiceRead.psrc') `
  -VisibleCmdlets 'Get-Service'
The creation commands produce files to review, not an assurance that the endpoint is safe. Inspect the generated capability and preserve its version. If narrower operations are required, write a reviewed wrapper with validated inputs rather than assume an optional cmdlet parameter restriction prevents every broader invocation.
Build a restricted session configuration
Create the approved local run-as group and confirm its minimal permissions. Do not populate it with powerful rights as a shortcut. Map only the designated domain support group to the capability. SessionType RestrictedRemoteServer provides the constrained session model; do not replace it with an unrestricted configuration to fix a connection error.
# Create the local group through the approved account process first.
$roles = @{
  'CORP\Server-Service-Observers' = @{
    RoleCapabilities = 'ManagedServiceRead'
  }
}
New-PSSessionConfigurationFile -Path 'C:\JEA-Config\ServiceObserver.pssc' `
  -SessionType RestrictedRemoteServer -RunAsVirtualAccount `
  -RunAsVirtualAccountGroups 'JEA-ReadOnly-Operators' `
  -TranscriptDirectory 'E:\JEA-Evidence' -RoleDefinitions $roles
Test-PSSessionConfigurationFile -Path 'C:\JEA-Config\ServiceObserver.pssc'
Create and protect the configuration and transcript directories beforehand. The named group must exist and fit the required access. A read-only service query normally needs much less than local administration; test the actual permissions rather than relying on a broad token.
Register and inspect the endpoint deliberately
Register the reviewed configuration under a distinct endpoint name during a maintenance window. Session registration can affect remoting service operation, so account for existing management sessions. Preserve the previous endpoint list and do not overwrite the ordinary administrator configuration.
Get-PSSessionConfiguration | Select-Object Name,Permission
Register-PSSessionConfiguration -Name 'Managed-Service-Observer' `
  -Path 'C:\JEA-Config\ServiceObserver.pssc'
Get-PSSessionCapability -ConfigurationName 'Managed-Service-Observer' `
  -Username 'CORP\pilot-observer'
Inspect the effective capability for a representative delegated user. Group membership and endpoint ACLs both matter. An installed role file that no eligible endpoint uses does not delegate anything, while an overly broad endpoint ACL can allow unintended callers. Record both the authentication boundary and command boundary.
Prove allowed and denied behaviour as the delegated user
Connect with the intended user rather than testing only as the administrator who created the endpoint. Read service status, inspect the available commands and confirm that unrelated actions are unavailable. Use harmless negative tests; do not attempt an actual destructive operation as a demonstration.
Enter-PSSession -ComputerName 'app-pilot01.corp.example' `
  -ConfigurationName 'Managed-Service-Observer'
# Inside the delegated session:
Get-Command
Get-Service -Name W32Time
Exit-PSSession
Confirm the transcript is written and retained under its intended access policy. Verify that an out-of-group account cannot connect. The visible command list and successful service query demonstrate this pilot’s behaviour, not a blanket guarantee about every future function added to the module.
Inspect effective identity only through approved diagnostics. Do not expose arbitrary shell executables just to obtain whoami output, since that can introduce a wider execution capability than the endpoint is meant to provide.
Review capabilities as code, including escape routes
External programs, providers, file access and functions can create unintended ways to execute or modify code. A wrapper that accepts arbitrary paths or command text can defeat a narrow visible-command list. Validate input, avoid string-based command construction and test unusual but harmless parameter combinations.
Capabilities from multiple roles can combine, so a user in several mapped groups may receive more than one role suggests alone. Review effective permissions for real memberships. Keep configuration and module deployment controlled and repeat tests after updates. A signature can support provenance but does not make an unsafe function safe.
For network access, understand the run-as identity and second-hop implications. Do not enable broad delegation merely because a read-only endpoint unexpectedly needs a share. Reassess the operation or use a deliberately scoped service identity where justified.
Withdraw access without losing the recovery path
If the pilot fails, use the independent administrator route to unregister only the new endpoint and preserve configuration and transcripts. Do not disable all WinRM or delete the module while another endpoint depends on it. Verify normal approved administration remains available.
# After dependency review and the approved pause/removal decision:
Unregister-PSSessionConfiguration -Name 'Managed-Service-Observer'
Document permitted commands, run-as group, eligible users, file ownership, logging and version. The managed result is a small, demonstrable support boundary that can be maintained and removed deliberately, rather than a renamed unrestricted PowerShell session.
 Running scheduled PowerShell under a deliberate service identity
Register a scheduled PowerShell job with an approved service identity, protected code and explicit run settings, then verify the stored…
 Collecting consistent results from several Windows servers with PowerShell
Run a bounded PowerShell operation across explicit server names, retain structured per-host results and failures, understand serialised…
 Collecting PowerShell transcripts without creating a new secret store
Deploy PowerShell transcription as protected evidence collection, distinguish shell and event-log coverage, test real writing contexts and…
 Signing a PowerShell release with a trusted code-signing identity
Sign a reviewed PowerShell release with an explicitly authorised key and timestamp service, verify provenance and trust on target servers,…
