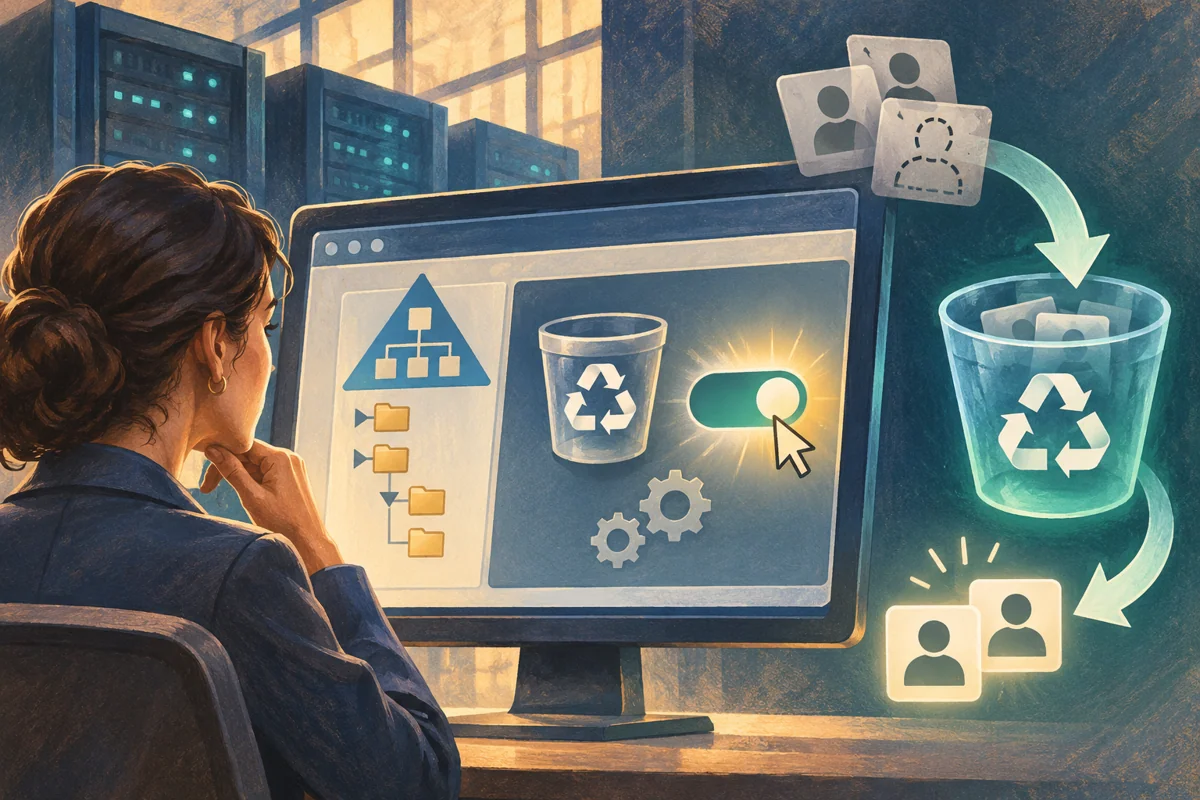
Recovering the original directory object is different from creating another account with the same name. Applications and permissions can depend on the original identity and its retained relationships. Active Directory Recycle Bin provides a supported recovery route for eligible deletions, provided it was enabled before the deletion and the object remains within its recoverable lifecycle.
On a managed environment, report an accidental deletion immediately with the affected user or group and approximate time. Netcloud24's authorised administrators assess the directory state and coordinate recovery. Customers do not need to change forest features or attempt a restore through an administrative desktop.
First establish what changed
Confirm that the incident was a deletion rather than a rename, move, disablement or modified attribute. Recycle Bin is not a general history browser for reversing every edit to an existing object. Record its former location, purpose, known GUID or SID and the business owner.
Check whether someone has already recreated an object with a similar name. A new account does not become the deleted identity simply because its display name matches. A restoration conflict needs an explicit decision rather than a broad bulk command.
Include connected systems in the assessment. Mail services, synchronisation tools and applications can have independent deletion workflows. Restoring on-premises AD does not automatically reverse every action they have taken.
Confirm feature state and recovery limits
Get-ADOptionalFeature -Identity 'Recycle Bin Feature' |
 Select-Object Name,EnabledScopes
Get-ADForest | Select-Object Name,ForestMode
Get-ADDomain | Select-Object DNSRoot,DomainMode
Use a suitable authorised Active Directory management context. In a multidomain forest, confirm the relevant domain explicitly. A feature enabled somewhere in a different environment offers no protection for this object's deletion.
Objects deleted before enablement do not become eligible retroactively. Retention is also finite: directory lifecycle and garbage-collection settings determine how long an object remains restorable through this method. Verify the actual state rather than relying on an assumed universal number of days.
Maintain AD-aware backups and forest-recovery arrangements even when Recycle Bin is active. It does not replace recovery from corruption, widespread malicious changes or loss of the directory infrastructure.
Enablement is a separate irreversible decision
If the organisation has not enabled the feature, plan that forest-level change for future protection. The documented feature prerequisite is Windows Server 2008 R2 or later functional levels, with suitable administrative authority and tools. Modern controller introductions can have stricter functional-level requirements of their own.
Check replication health and current recoverable backups before changing optional forest features. Do not raise functional levels silently to satisfy a checklist. Record the scope and obtain the organisation's authorisation for the irreversible operation.
$currentForest = Get-ADForest
Enable-ADOptionalFeature -Identity 'Recycle Bin Feature' `
 -Scope ForestOrConfigurationSet -Target $currentForest.Name
Inspect the confirmation carefully: the feature cannot subsequently be disabled. Allow replication and verify EnabledScopes. A successful command is not a reason to skip a controlled recovery exercise.
Rehearse with a harmless object
Use an approved test OU and a clearly identified test account or group. Record its identity and intended relationships before deleting it. Never delete a real employee or production privilege group simply to demonstrate a recovery feature.
In Active Directory Administrative Center, locate the relevant domain's Deleted Objects container and inspect the exact test object. Restore it using the supported workflow and compare the resulting location, attributes and harmless test memberships with the baseline.
Retain the result without claiming that it validates every application integration. The directory restore and an external application's recovery are separate checks. Clean up the test objects through the agreed process after the exercise.
Select a real deleted object precisely
Browse or query candidates for review, but do not pipe a broad name search straight into restoration. Similar names, historical accounts and deleted containers can all appear in an investigation. A GUID-based selection makes the chosen identity explicit.
$reviewedGuid = Read-Host 'Reviewed deleted-object GUID'
$object = Get-ADObject -Identity $reviewedGuid -IncludeDeletedObjects `
 -Properties isDeleted,lastKnownParent,whenChanged
$object | Select-Object ObjectGUID,Name,ObjectClass,isDeleted,lastKnownParent,whenChanged
Confirm it is the intended deleted object, check the original parent and resolve any naming conflict. Keep the deletion context and approval with the case. Restoration can reinstate access, so it deserves authorisation as well as technical accuracy.
If a parent OU was also deleted, restore the required hierarchy in a supported order or select an explicitly approved alternate target. Do not restore an entire subtree merely because doing so avoids one parent-path error.
Restore and verify the directory result
Restore-ADObject -Identity $object.ObjectGUIDInspect the restored object through the relevant controller, then allow replication and verify where dependent services obtain their view. Check its GUID or SID, location, enabled state, restrictions and group relationships rather than looking only for a familiar display name.
For an account deleted during a security incident, recovery should not automatically reinstate unrestricted use. Coordinate credential and access decisions with the incident owner. For an accidental business deletion, perform a controlled authentication and resource-access test appropriate to the account.
Ask connected-system owners to check their own state, including mailbox, licence, profile or application record where applicable. Those services may have different retention windows and supported recovery actions.
Handle unavailable objects and failed restores
If nothing is found, examine the domain, permissions, feature-enablement time and retention state. Confirm that deletion actually happened. If the feature cannot recover the identity, use the documented broader recovery assessment rather than inventing a substitute account as an automatic fix.
For a restore error, preserve the exact message and object identifier. Investigate parent availability, name conflicts, rights and replication. Repeating a wide restore command can create additional unintended changes.
A restored object can be deleted again only as a new reviewed directory action. That is not an invisible cancellation. Likewise, cleaning up a test restore does not reverse the forest-wide decision to enable Recycle Bin.
Microsoft explains the feature's lifecycle in its Recycle Bin guide. Related planning includes controller replacement and group-change auditing.
Retain the recovery decision
Keep the reviewed object identifier, authorising owner, restoration time and dependent-system checks together. This makes it possible to distinguish an intentional restoration from an unexplained return of access during a later security review.
 Designing and promoting the first controller in a new AD forest
Prepare a new Active Directory forest with reviewed naming, functional levels and recovery. Install AD DS, run prerequisite checks, promote…
 Introducing an additional domain controller into a healthy directory
Introduce a writable controller only after directory health, functional compatibility and preparation rights are verified. Test promotion,…
 Creating protected organisational units with clear policy boundaries
Create an AD organisational unit for a defined delegation or policy purpose. Review inheritance, use a protected creation, verify placement…
 Provisioning an Active Directory user without exposing credentials
Provision an approved AD user through unique identifiers, a secure credential prompt and staged access review. Verify group membership,…
 Separating staff roles from resource permissions with AGDLP
Apply AGDLP by separating individual accounts, business-role groups and resource entitlements. Inventory existing permissions, build the…
