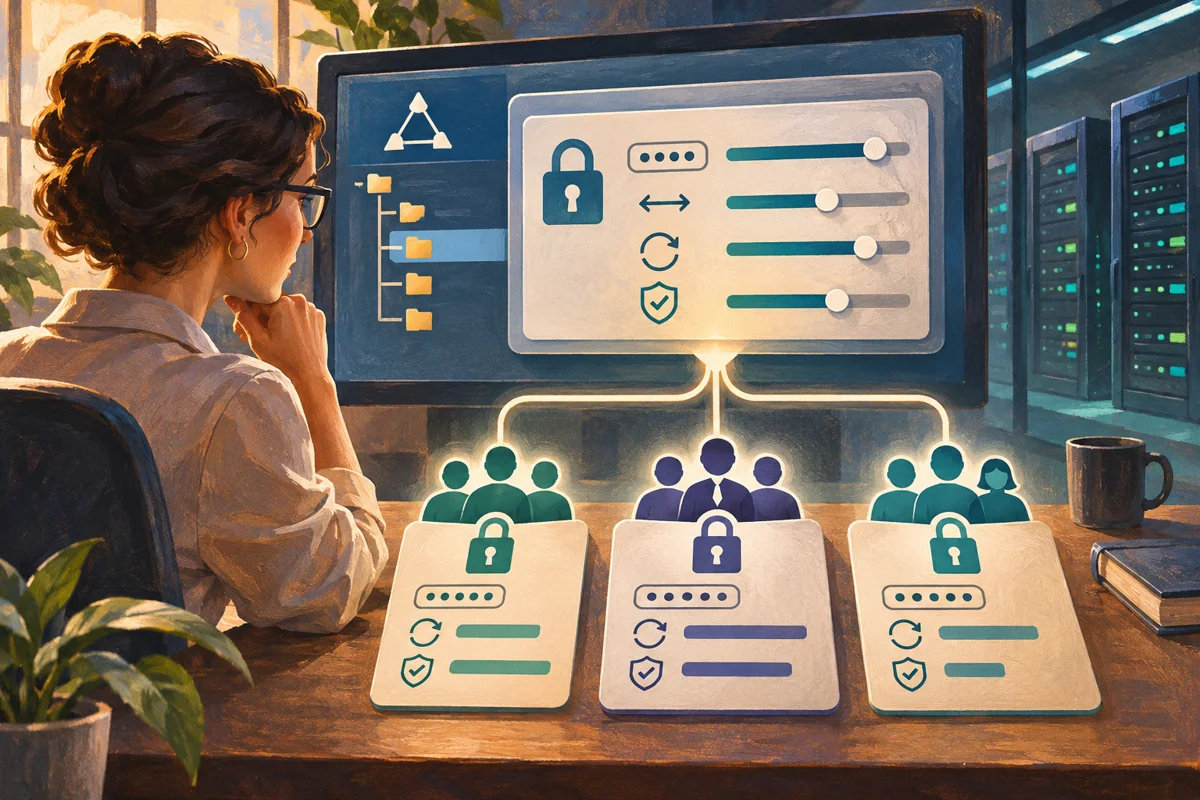
A user can belong to several groups with password settings objects yet receive only one resultant fine-grained policy. That makes assignment and precedence as important as the password values themselves. Begin with a defined user population and a way to prove the winning policy, rather than linking a password GPO to an OU and assuming it creates the exception.
Fine-grained policy is a directory administration task. Netcloud24 handles the agreed managed configuration; customers provide their account requirements and approval criteria. Ordinary users should follow the resulting sign-in process, not attempt to alter domain password settings.
Choose the population and the control
A password settings object, or PSO, can apply to AD user objects and global security groups. It does not directly target an organisational unit. If business membership follows an OU or department, maintain the appropriate explicit global-group membership through a controlled process.
The feature changes domain password and lockout policy for its subjects. It does not introduce MFA, protect local accounts automatically or control every application password store. Those controls require their own management arrangements.
Review service identities separately. A new expiry or lockout rule can interrupt a traditional service account, even if the human-user policy is sensible. Confirm whether a managed service identity is more suitable before treating every account as an ordinary employee.
Inspect the current effective picture
Get-ADDomain | Select-Object DNSRoot,DomainMode
Get-ADDefaultDomainPasswordPolicy
Get-ADFineGrainedPasswordPolicy -Filter * |
 Select-Object Name,Precedence,MinPasswordLength,LockoutThreshold
Check documented functional and tool prerequisites for the management path. Microsoft's current configuration guide lists a Windows Server 2012 or later domain functional level and suitable AD administration tools. Use the required delegated authority rather than increasing unrelated application operators' privileges.
Record existing assignments, direct-user exceptions and group overlaps. A policy list alone cannot establish an individual's result. Query representative users, including those who already have special requirements, and retain the baseline.
If no PSO applies, the default domain password policy remains relevant. An empty fine-grained resultant result does not mean the account has no password controls.
Make precedence explainable
Direct assignment to a user takes priority over group-derived selection. Within the relevant selection stage, lower numerical precedence has higher priority. A policy named Executive or Secure does not win because of its name.
Avoid equal values where policy applicability overlaps. Although the directory has tie-breaking behaviour, a design dependent on it is unnecessarily difficult to review. Choose a documented numbering convention and reserve room for future changes.
Review the effect of adding another PSO later. A new overlapping assignment can change a user's result without editing the older object. Include resultant-policy verification in every new exception, not just initial deployment.
Create a small pilot before assignment
Prepare an owned global security group, for example GG-Finance-Password-Pilot, containing only approved test users initially. Create the policy independently, review it and only then associate the subjects.
The following values illustrate the mechanics. They are not a recommendation for periodic expiry or a universal security baseline; substitute the organisation's approved requirements.
New-ADFineGrainedPasswordPolicy -Name 'PSO-Finance-Pilot' `
 -Precedence 30 -MinPasswordLength 15 -PasswordHistoryCount 24 `
 -ComplexityEnabled $true -ReversibleEncryptionEnabled $false `
 -MinPasswordAge (New-TimeSpan -Days 1) `
 -MaxPasswordAge (New-TimeSpan -Days 120) `
 -LockoutThreshold 10 `
 -LockoutObservationWindow (New-TimeSpan -Minutes 20) `
 -LockoutDuration (New-TimeSpan -Minutes 20)
Check every value, including compatibility with the chosen password length and application estate. Keep reversible encryption disabled unless a documented exceptional requirement has been approved. It is not needed for ordinary Windows password authentication.
Prepare help-desk guidance for expiry and lockout behaviour before involving live users. A technically correct policy can still create avoidable disruption if stale stored credentials immediately trigger failures.
Associate subjects and prove the result
Add-ADFineGrainedPasswordPolicySubject -Identity 'PSO-Finance-Pilot' `
 -Subjects 'GG-Finance-Password-Pilot'
Get-ADFineGrainedPasswordPolicySubject -Identity 'PSO-Finance-Pilot'
Get-ADUserResultantPasswordPolicy -Identity 'PolicyValidation' |
 Select-Object Name,Precedence,MinPasswordLength,MaxPasswordAge,LockoutThreshold
Use a real approved test identity in place of the illustration. Allow replication, and inspect the controller relevant to the test where appropriate. Repeated workstation gpupdate commands do not correct a missing directory association or broken AD replication.
Inspect the user's PasswordLastSet, PasswordNeverExpires and LockedOut properties where relevant. These help explain behaviour that a PSO's name alone cannot. Do not remove an exemption or unlock an account casually to make a test proceed.
Test observable behaviour without locking out colleagues
Use a dedicated account for controlled password-change tests. Verify acceptance and rejection through a secure process without logging the candidate secrets. Other password filters can contribute to a rejection, so preserve the actual error and support context.
Lockout testing should be explicitly authorised and isolated. Repeated failures against a production administrator can deny service and trigger security response. Agree the sequence, expected recovery and monitoring notification before testing.
A new minimum does not rewrite existing passwords. Age settings and account properties can nevertheless affect users operationally, so test more than the first successful query. Include an account with overlapping policy groups and a direct exception if those exist in the design.
Expand, monitor and reverse deliberately
Roll out membership in manageable stages and query representative resultant policies. Watch lockouts, failed authentication and service failures with the security and support teams. Distinguish expected user transition issues from unrelated attacks or application faults.
Retain the approved values, subject group, precedence rationale, owners and test evidence. Reconcile group membership during account-role changes so users do not keep an unintended exception after moving jobs.
To withdraw the change, remove the intended subject association and verify the new result before deleting the PSO. Falling back to another object or the domain default can tighten or loosen controls. Reversal does not undo passwords already changed or failed service transactions.
Microsoft documents resultant-policy selection and configuration prerequisites. See also traditional service-account management.
Review assignments as access changes
Changes to a PSO subject group are security-relevant administration, even when the group does not grant file access. Adding an account can alter password age and lockout behaviour. Monitor and authorise those membership changes, and avoid nesting arrangements that nobody can explain during support.
For exceptions, record an expiry or review date and an accountable owner. A policy introduced for one application migration can otherwise remain associated with users long after the original requirement disappears. Review both direct user assignments and group-derived results, since removing one group membership does not necessarily remove a direct PSO association.
 Designing and promoting the first controller in a new AD forest
Prepare a new Active Directory forest with reviewed naming, functional levels and recovery. Install AD DS, run prerequisite checks, promote…
 Introducing an additional domain controller into a healthy directory
Introduce a writable controller only after directory health, functional compatibility and preparation rights are verified. Test promotion,…
 Creating protected organisational units with clear policy boundaries
Create an AD organisational unit for a defined delegation or policy purpose. Review inheritance, use a protected creation, verify placement…
 Provisioning an Active Directory user without exposing credentials
Provision an approved AD user through unique identifiers, a secure credential prompt and staged access review. Verify group membership,…
 Separating staff roles from resource permissions with AGDLP
Apply AGDLP by separating individual accounts, business-role groups and resource entitlements. Inventory existing permissions, build the…
