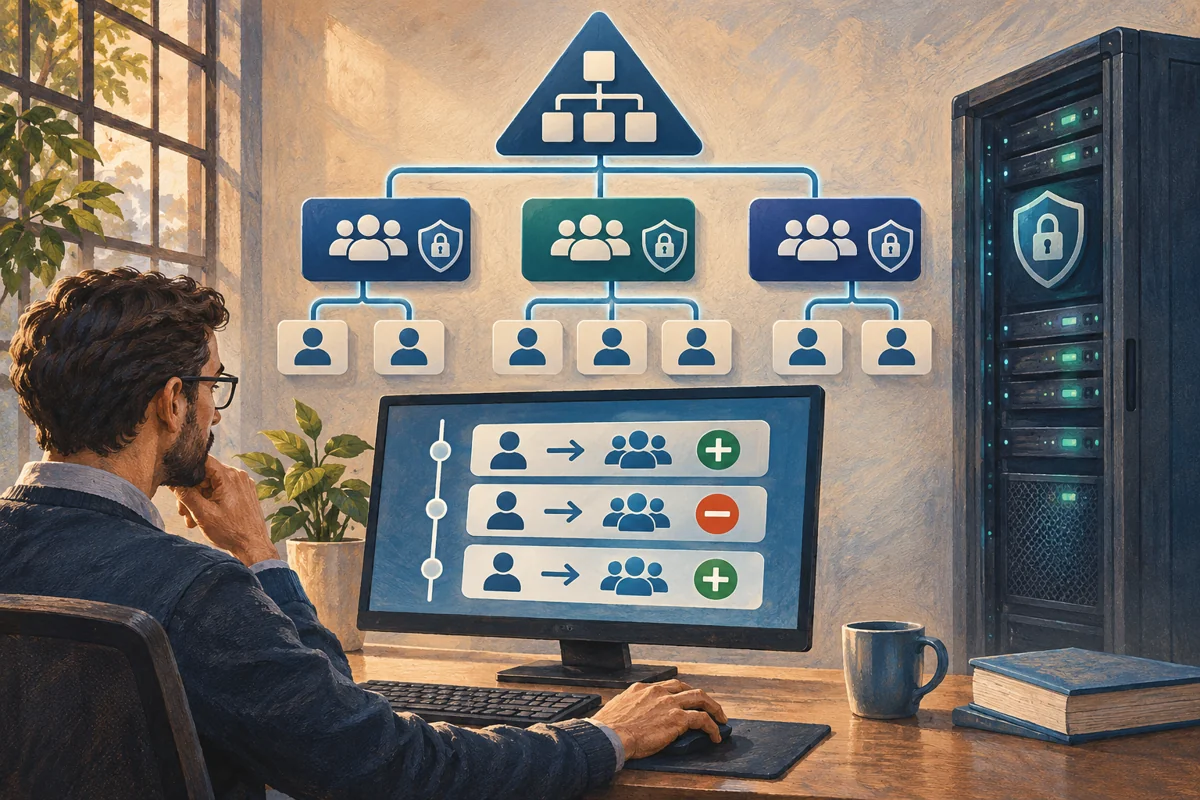
An investigation needs to distinguish the account whose access changed from the account that made the change. Those identities appear in different fields of a membership event. It also needs the right source computer: a domain controller records a domain-group change it processes, while a member server records changes to its own local groups.
This article explains an administrator's audit design and investigation workflow. Netcloud24 prepares the agreed managed security configuration; customers report an unexpected access change with its business context rather than enabling domain-wide auditing themselves.
Identify the access path you care about
List high-value groups, their scopes, owners and normal approval routes. Include administrative privileges, application access and sensitive file permissions. A group name alone can be misleading, so retain its SID and intended purpose.
Review nesting. A user added to an intermediate group can gain access through an unchanged privileged parent. Monitoring only direct edits to the parent misses this route. Keep relevant nested groups in scope and maintain a separate current membership baseline.
Decide which local groups on application hosts matter too. Watching every domain controller does not provide a complete history of local Administrators membership across the member-server estate.
Prepare the governing audit policy
Use an authorised account and a reviewed domain-controller GPO. Capture the previous settings and scope before making the change. In Advanced Audit Policy Configuration, review Account Management and Audit Security Group Management, including the relationship with legacy category settings.
Enable the success auditing needed for successful membership changes. Do not assume failure auditing creates a corresponding event for every denied attempt; the documented subcategory support determines what exists. Other authentication or directory evidence may be needed for failed administration.
Check whether the policy that gives audit subcategories precedence over legacy categories is configured consistently. Changing one setting without understanding the governing baseline can produce unexpected effective results.
auditpol /list /subcategory:*
auditpol /get /subcategory:"Security Group Management"
The displayed subcategory name is for an English installation. Use the installed listing where labels differ. Confirm the effective policy on the relevant controllers after refresh rather than relying solely on what the GPO editor displays.
Use event families appropriate to group scope
| Security group context | Member added | Member removed |
|---|---|---|
| Global domain group | 4728 | 4729 |
| Local or domain-local group | 4732 | 4733 |
| Universal domain group | 4756 | 4757 |
Interpret the originating computer and target fields alongside the identifier. Event 4732 on a member server and the same family on a controller can concern different group contexts. An event number without its source is incomplete evidence.
A controlled test should use a harmless test account and test group. Record the time, add the member and remove it again through an approved workflow. Do not test monitoring by temporarily granting Domain Admins or another production privilege.
Query a bounded incident window
On the relevant controller, or through an approved collection path, query the Security log around the incident:
$begin = (Get-Date).AddHours(-3)
Get-WinEvent -FilterHashtable @{
 LogName='Security'
 Id=4728,4729,4732,4733,4756,4757
 StartTime=$begin
} | Select-Object TimeCreated,Id,MachineName,RecordId,Message
A finite window is easier to correlate than an arbitrary last-ten-events query. In a busy domain, the last few records may exclude the actual incident entirely. Check time zones and clock consistency when combining sources.
If you do not know which controller handled the change, use the approved central collection or query the relevant controllers systematically. A missing record on one controller is not proof that no change occurred.
Read actor, member and group independently
Subject fields identify the security context that performed the action. Member fields identify the identity whose membership changed. Target fields identify the affected group. Confusing Subject with Member can incorrectly attribute an administrator's action to the employee gaining access.
Keep SIDs and original event XML. Names may be unresolved, renamed or rendered differently by localisation. For automation, parse named XML data fields rather than fixed property positions or a search for English wording.
$record = Get-WinEvent -FilterHashtable @{
 LogName='Security'; Id=4728; StartTime=$begin
} -MaxEvents 1
if ($record) {
 $xml = [xml]$record.ToXml()
 $fields = @{}
 foreach ($entry in $xml.Event.EventData.Data) {
  $fields[$entry.Name] = $entry.'#text'
 }
 $fields
}
This example inspects one matching event for illustration. A real investigation must select the relevant records, retain their full metadata and avoid assuming the newest event is the incident.
Correlate changes with the real workflow
Match the actor and timestamp with the approved access request, administrative session and any access-management automation. A service account can be the direct actor while another system initiated the business request. Investigate that chain before assigning responsibility to a person.
Include the source computer, log and record identifier in retained evidence. Record numbers are not globally unique across controllers. Preserve raw evidence through the approved export or SIEM process and protect access to it.
Check current membership as a separate observation. Event history explains recorded changes; a snapshot shows present state. Neither proves the other is complete, especially when collection or retention gaps exist.
Make central collection and alerts verifiable
Forward the selected evidence from every in-scope controller and relevant member server. Set retention around actual event rate and incident-response needs. A healthy-looking dashboard is insufficient if source logs overwrite records before forwarding catches up.
Build alerts around valuable groups, unusual actors and unexpected timing, with a named response owner. Include the affected group and member rather than sending an unexplained numeric identifier. Test the harmless event end to end in the central system.
Monitor collection delay and subscription health separately from the alert rule. A correct rule cannot react to an event it never receives, and a delay of several hours may defeat a rapid-response objective.
Resolve gaps without erasing history
If evidence is missing, check whether the change occurred, which computer processed it, effective success auditing and the selected time window. If it exists locally but not centrally, investigate forwarding independently. Do not repeatedly change audit scope to compensate for a collector fault.
Rollback restores the recorded policy in its governing GPO and verifies effective settings after refresh. Clearing Security logs is not rollback. Microsoft documents the membership event families and named membership fields. See also password-policy assignment.
 Designing and promoting the first controller in a new AD forest
Prepare a new Active Directory forest with reviewed naming, functional levels and recovery. Install AD DS, run prerequisite checks, promote…
 Introducing an additional domain controller into a healthy directory
Introduce a writable controller only after directory health, functional compatibility and preparation rights are verified. Test promotion,…
 Creating protected organisational units with clear policy boundaries
Create an AD organisational unit for a defined delegation or policy purpose. Review inheritance, use a protected creation, verify placement…
 Provisioning an Active Directory user without exposing credentials
Provision an approved AD user through unique identifiers, a secure credential prompt and staged access review. Verify group membership,…
 Separating staff roles from resource permissions with AGDLP
Apply AGDLP by separating individual accounts, business-role groups and resource entitlements. Inventory existing permissions, build the…
