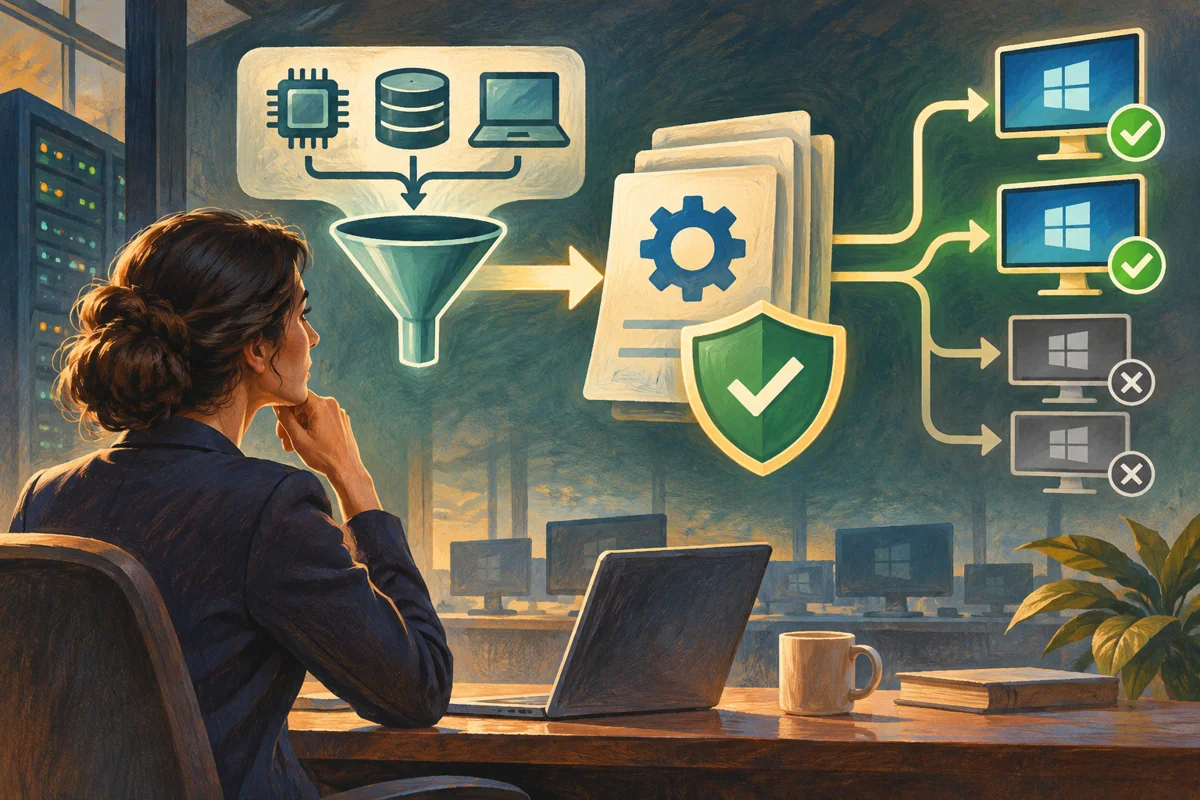
A WMI filter can make one GPO apply only when a target computer satisfies a query. That is useful for a specific property that ordinary OU or security-group scope cannot express cleanly. It also adds a runtime dependency and can cause slow or missing policy processing if the query is expensive, unsupported or based on a mistaken version assumption.
Netcloud24's managed team handles the agreed policy targeting. Customers specify which systems need the behaviour, rather than editing WMI or broad domain policy themselves. The following workflow is for the authorised administrator choosing and validating a filter.
Decide whether a query is necessary
Use OU and security filtering where they already describe a stable, owned population. A list of application hosts maintained in an asset process may be clearer than a query guessing from installed components. WMI filtering is not a replacement for an accurate inventory.
Write the intended condition in ordinary language first: member servers, a particular supported OS build or another documented property. Define expected positive and negative examples. If nobody can identify a machine that should fail the condition, the scope is not yet reviewable.
Consider what happens on future releases. A filter that selects only today's builds can silently exclude a replacement server next year. Decide whether the condition represents a durable role or an intentionally limited version cohort.
Use properties with understood meaning
The Win32_OperatingSystem class provides Version, BuildNumber and ProductType. Workstations, domain controllers and other servers have different ProductType values. A member-server condition is not the same as “all Windows Servers”, because it excludes controllers.
Windows Server releases can share a major version family. Testing Version like 10.% does not distinguish Server 2016, 2019, 2022 and 2025 by itself. Build and other properties must be interpreted against the actual supported releases if version-specific targeting is required.
Be careful with string comparisons and wildcards. A greater-than test on a string property may not mean numeric version ordering. Prefer explicit documented logic and validate it on every intended positive and negative class.
Test a simple query locally
For illustration, this query selects version-10-family member servers, not every server release and not domain controllers:
$query = 'SELECT * FROM Win32_OperatingSystem WHERE Version LIKE "10.%" AND ProductType = 3'
Get-CimInstance -Namespace root\CIMV2 -Query $query
Use a representative intended member server and a computer that should not match. Inspect the returned properties instead of treating any object as proof the condition is correct. Repeat on the actual builds present in the rollout.
A valid empty result and a provider error are different outcomes. Capture errors and timing. A condition that works only on the administrator's workstation is not ready to determine server policy.
Avoid expensive or disruptive inventory classes
Keep queries narrow and inexpensive. Do not casually query Win32_Product for installed software during policy processing: its provider can trigger Windows Installer consistency activity and is not a comprehensive inventory of every application technology.
For application membership, a controlled group or supported deployment signal is often more reliable. A product name may vary by version, architecture or installer, creating unexpected exclusions even before performance is considered.
Review queries that traverse large associations or depend on fragile providers. Every target must evaluate its applicable filter, so a modest delay multiplied across logons can become an operational problem. Measure the actual processing effect rather than relying on a query that eventually finishes in a manual console.
Create an owned filter and attach it deliberately
In Group Policy Management, open WMI Filters, create a descriptive filter and record its purpose, owner and tested query. Use the correct namespace, commonly root\CIMV2 for the example class. Do not leave unexplained copied query fragments in the definition.
Attach the filter to the intended pilot GPO and confirm the selected filter name. One GPO has one associated WMI filter; a filter can contain multiple queries, which must be designed with their documented combined evaluation in mind. Avoid using that facility to hide a long, hard-to-review targeting scheme.
Preserve existing security filtering and permissions. The WMI result is another condition, not an alternative grant of access. A true query cannot make a GPO apply when ordinary scope or permissions exclude the target.
Prove the GPO result, not just the query
Apply the approved pilot setting and collect resultant-policy evidence from an intended target. Confirm the filter evaluates as expected and the setting wins. Test a negative target where the GPO must remain excluded.
gpresult /scope computer /h C:\Windows\Temp\WmiFilter-ComputerPolicy.htmlUse an authorised context and protect the report. For user settings, understand that WMI evaluates on the processing computer, not as a directory search over the user's department. Loopback can add another scope consideration on shared hosts.
Inspect GroupPolicy/Operational events and processing duration. A test showing the right registry value does not establish acceptable sign-in performance or explain whether another GPO supplied that value instead.
Investigate false and failed evaluations separately
Unexpected false results call for checking the property values, namespace, query syntax and target OS. Errors call for provider and WMI diagnostics. Do not rebuild the entire WMI repository as a routine response to one copied filter failing.
If policy is slow, compare with the filter removed in a controlled pilot and inspect the query cost. Retain the original configuration and evidence. An unrelated provider timeout can look like a Group Policy issue unless the actual evaluation is examined.
Maintain and reverse the condition
Record the tested releases and review the filter when new server versions or application deployments arrive. Keep a named owner so obsolete version restrictions do not silently exclude new production hosts.
Before removing the filter, consider the resulting wider GPO scope. Detaching a restrictive filter can cause settings to apply to every otherwise eligible target. Disable or rescope the pilot safely, then verify the intended result and any persistent preference effects.
Microsoft documents WMI-filter creation and software-query limitations. See also server inventory for collecting target properties independently.
Include negative test results in the handover, since a passing target alone cannot reveal an expression that matches too broadly.
 How to Create and Link a Group Policy Object with PowerShell
Applies to: Windows Server 2019, 2022 and 2025 domain environments.A GPO should…
 How to Back Up and Restore Group Policy Objects
Applies to: Windows Server 2019, 2022 and 2025 domain environments.GPO backup protects…
 How to Configure Group Policy Loopback Processing for RDS Servers
Applies to: Windows Server 2019, 2022 and 2025 domain…
 How to Configure Domain Password and Account Lockout Policy
Applies to: Windows Server 2019, 2022 and 2025 domain environments.Domain…
 How to Troubleshoot Group Policy with GPResult and Event Viewer
Applies to: Windows Server 2019, 2022 and 2025 domain environments.Group…
