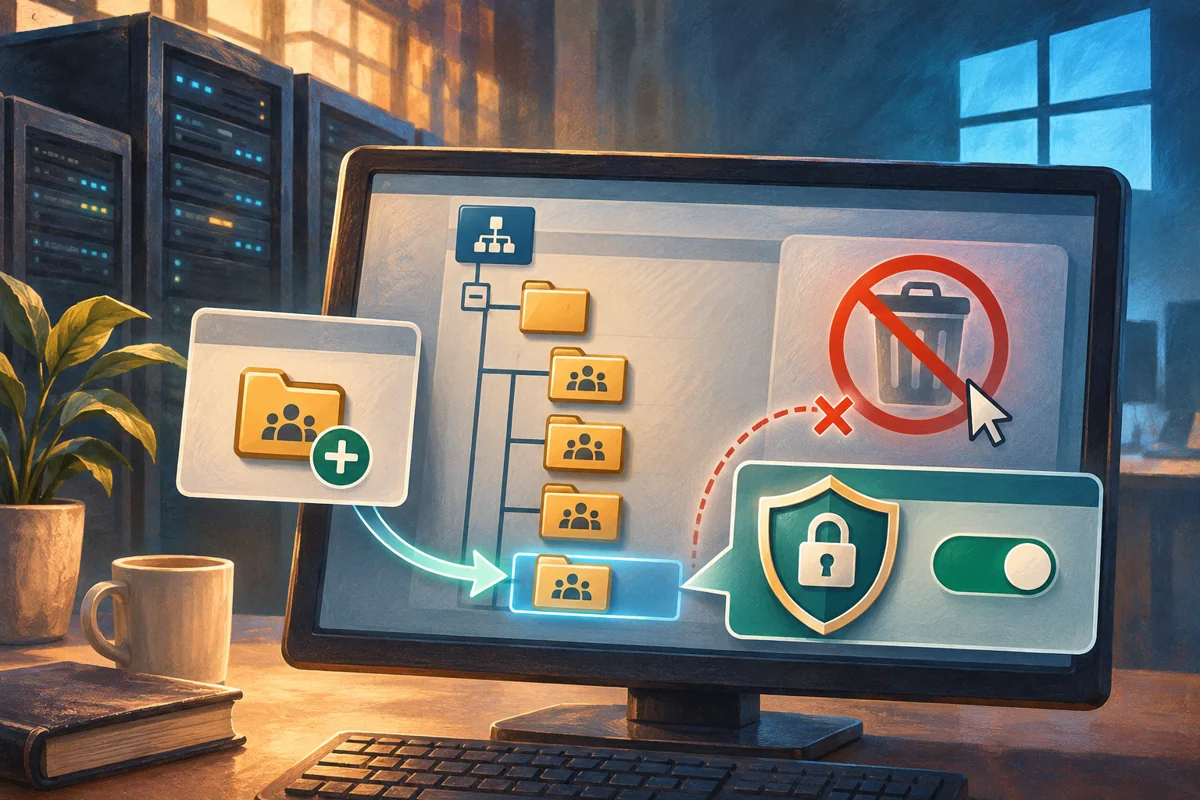
An organisational unit is useful when it gives Active Directory a clear administration or policy boundary. It should express a reason for placing objects together, not reproduce every changeable detail of an organisation chart. Plan the boundary before creating another directory container.
This article applies to authorised AD DS administrators working with Windows Server 2019, 2022 or 2025. Netcloud24 prepares agreed directory organisation for Managed environments. Customers should provide user roles and ownership requirements rather than create or move OUs independently.
Give the OU a specific job
Decide whether the OU supports delegated administration, Group Policy targeting or a documented lifecycle process. Separate ordinary users, privileged identities and server roles where the security and management design requires different treatment.
An OU is not a security group. Putting an account in an OU does not automatically grant access to an application or folder. Groups express permissions; OU placement influences directory management and policy scope.
The default Users container is also not an ordinary OU for policy linking. Check the actual object type instead of assuming every folder displayed in a directory console has identical capabilities.
Review inherited settings before choosing placement
A child OU inherits relevant policy and security relationships from its position. Review parent GPO links, enforcement and delegation before selecting a path. A tidy-looking tree can still deliver an inappropriate policy to a production server.
Moving an existing object is a separate change. It can alter the effective policy even though its name and group memberships remain unchanged. Test representative objects and coordinate with application owners before moving a whole population.
Keep the hierarchy understandable. Deep nesting can make ownership and effective settings difficult to explain. Use enough structure to express the real boundaries without creating a unique OU for every small exception.
Confirm rights and the target directory
Use the ActiveDirectory module on a supported management device and a credential delegated for the intended parent. Creating an OU does not usually require a forest-wide administrative identity simply because the task is performed in AD.
Verify the domain and healthy writable controller. In an environment with several domains, an implicit default can select the wrong context. Record the target controller and parent distinguished name explicitly.
Import-Module ActiveDirectory
Get-ADDomain | Select-Object DNSRoot, DistinguishedName
Get-ADOrganizationalUnit -Filter * |
    Select-Object Name, DistinguishedName
Use the results to identify the real path. The illustrative examples below use a documentation namespace and must be replaced with approved values.
Check the proposed parent and name
$server = 'dc01.ad.business.example.org'
$parent = 'DC=ad,DC=business,DC=example,DC=org'
Get-ADObject -Identity $parent -Server $server
Get-ADOrganizationalUnit -Filter 'Name -eq "ManagedUsers"' -Server $server
Check whether a same-named OU already exists and where it is located. A duplicate name elsewhere may be valid but can confuse scripts or humans who select only by display name.
Confirm naming and descriptions with the directory standard. Use non-sensitive purpose information and ownership references, not passwords, recovery details or confidential customer data.
Create the reviewed protected OU
Preview the exact operation:
New-ADOrganizationalUnit -Name 'ManagedUsers' -Path $parent `
    -Server $server -ProtectedFromAccidentalDeletion $true `
    -Description 'Approved ordinary-user policy and delegation boundary' -WhatIf
WhatIf describes the request; it does not prove that every resulting policy is suitable. Once the design and rights are confirmed, apply the reviewed command without WhatIf and capture the resulting distinguished name.
Explicit protection makes the intended state clear even where creation defaults already provide it. Protection helps resist accidental deletion; it is not a backup, an absolute barrier against an authorised change or a substitute for permission review.
Verify placement and protection
$ou = 'OU=ManagedUsers,DC=ad,DC=business,DC=example,DC=org'
Get-ADOrganizationalUnit -Identity $ou -Server $server `
    -Properties ProtectedFromAccidentalDeletion,Description |
    Select-Object DistinguishedName, ProtectedFromAccidentalDeletion, Description
Expect the approved path, description and protection state. Verify through the chosen writable controller first, then confirm normal replication makes the object visible where operationally required.
Do not force broad replication merely because another console refreshed before replication completed. Compare timing and controller selection, then diagnose persistent inconsistency through the replication process.
Add delegation and policy through separate approvals
Create only the delegation needed by the responsible team. Review the exact object types and actions, including whether rights inherit to descendants. Do not grant broad domain control because an OU owner needs to reset ordinary user passwords.
Link approved GPOs through a staged policy process. Start with a representative test object and verify effective settings before moving production accounts. Keep OU creation, delegation and GPO content as distinct recorded actions.
For example, a server OU can receive a different management baseline from ordinary users. A newly created server placed there should be tested for access and application health before the same placement is applied to a large existing fleet.
Handle accidental-deletion protection deliberately
If a planned move or removal is blocked, verify the intended operation and approval. Do not disable protection throughout the hierarchy as a convenient workaround. Narrow any temporary change to the precise reviewed object and restore protection where required afterward.
Protection-related denial can involve the object and its parent permissions. Inspect effective security rather than assuming every access-denied message means the current user needs Domain Admin membership.
Do not use recursive deletion in a generic recovery example. An OU can contain users, groups, computers and policy relationships whose removal affects the whole service.
Retire or correct the structure safely
If the OU was created incorrectly, review its contents, delegation and GPO relationships before removal or renaming. Moving populated objects back can alter policy again, so retest the affected workflow.
Keep the final hierarchy, purpose and owner in the directory design record. Review it when services or support responsibilities change instead of allowing historical exceptions to accumulate without explanation.
See GPO linking and Microsoft’s New-ADOrganizationalUnit reference for supported creation parameters.
 Designing and promoting the first controller in a new AD forest
Prepare a new Active Directory forest with reviewed naming, functional levels and recovery. Install AD DS, run prerequisite checks, promote…
 Introducing an additional domain controller into a healthy directory
Introduce a writable controller only after directory health, functional compatibility and preparation rights are verified. Test promotion,…
 Provisioning an Active Directory user without exposing credentials
Provision an approved AD user through unique identifiers, a secure credential prompt and staged access review. Verify group membership,…
 Separating staff roles from resource permissions with AGDLP
Apply AGDLP by separating individual accounts, business-role groups and resource entitlements. Inventory existing permissions, build the…
 Enabling AD Recycle Bin as an irreversible forest change
Plan AD Recycle Bin as an irreversible forest feature. Verify prerequisites, scope and replication, understand pre-existing deletion limits…
