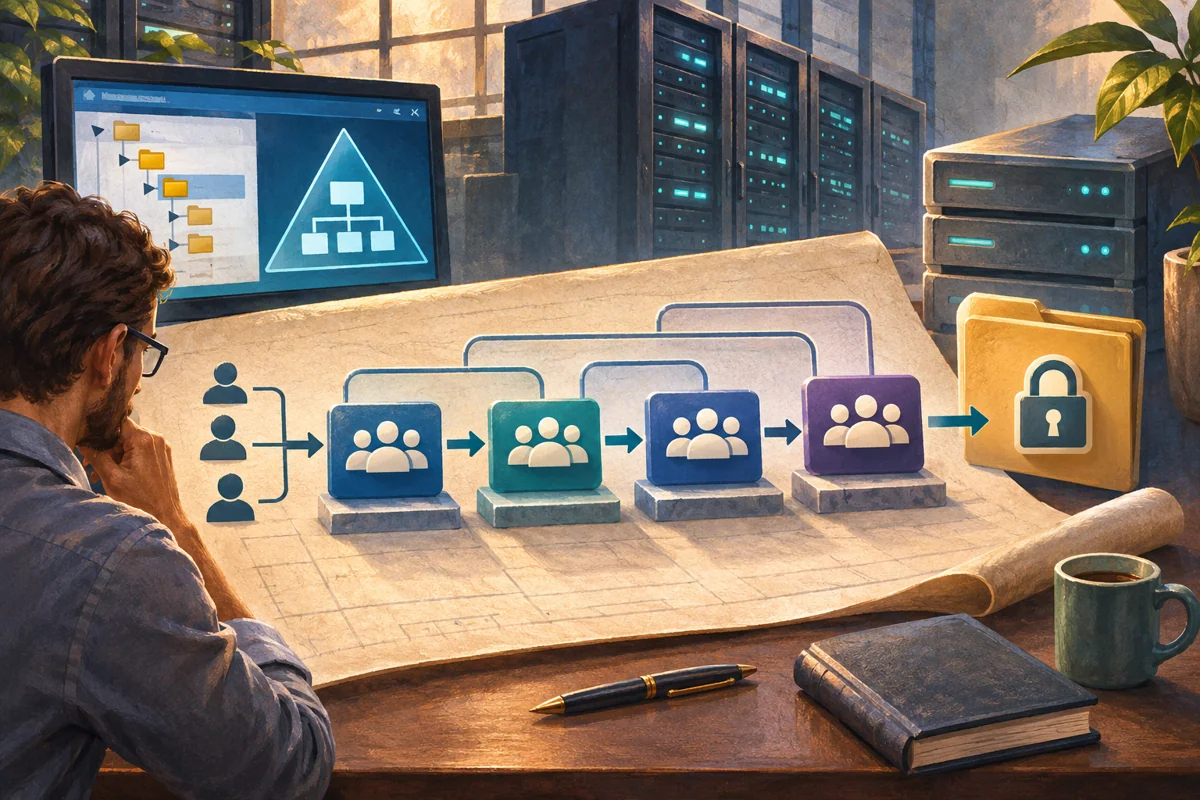
A permission model is easier to review when a person’s job and a resource’s access level are represented separately. AGDLP provides that separation in a common single-domain Active Directory design: Accounts join Global role groups, those groups join Domain Local resource groups, and permissions are assigned to the resource groups.
This administrator guide applies to AD DS environments using Windows Server 2019, 2022 or 2025. Netcloud24 prepares agreed users and permissions for Managed services. Customers describe business roles and approve access; they are not expected to construct the underlying directory group model themselves.
Start with a resource and an access decision
Identify the resource, data owner and permitted actions. Reading reports is different from modifying source files or administering an application. Name those decisions before choosing group names.
Keep access levels narrow enough to express real responsibilities. Full Control should not be the default answer for staff who need to update documents. A permission name must correspond to the actual effective rights on the resource.
Review both share and NTFS permissions for SMB data. Effective access depends on their combination and other relevant group memberships, not only the new directory group being added.
Understand the four parts
Accounts identify individual users or approved service principals. Avoid shared human identities and direct user entries scattered across resource ACLs.
Global groups collect the accounts that perform a business role within their permitted domain scope. Their membership should change when people join, leave or change responsibilities.
Domain Local groups represent a particular resource and access level in the resource domain. Their members can include approved role groups. Domain Local is an AD group scope, not the same as a machine-local group on one server.
Permissions are assigned to that resource group through the resource’s supported ACL or authorisation interface. Nesting groups alone does not create a share or grant rights automatically.
Keep the example intentionally single-domain
Consider a reporting team needing Modify access to an agreed departmental folder. A global group can express Reporting Staff, while a domain-local group expresses that folder’s Modify entitlement.
Cross-domain, forest and hybrid identity designs can require other scope and trust considerations, including universal groups. Do not stretch a single-domain example into a universal rule for every connected service.
Cloud roles and some applications have their own authorisation models. Confirm whether they consume AD nesting and which group scopes they support before adopting the same structure mechanically.
Inventory existing grants first
Record the resource’s current ACLs and relevant groups. Identify direct user grants, broad inherited access and nested privileges that could bypass the intended new model.
Agree how existing legitimate access will be preserved during migration. Adding a clean group does not remove old permissions, and deleting them too early can interrupt work. Use a staged reviewed change rather than resetting an entire ACL to a guessed baseline.
Get-ADGroup -Filter 'Name -like "*Reporting*"' `
    -Properties GroupScope,GroupCategory,Description |
    Select-Object Name,GroupScope,GroupCategory,Description
Use healthy directory context and an identity delegated for the group OU. Avoid creating duplicates because an existing group name is unfamiliar; inspect ownership and nesting first.
Create explicit security groups
The following examples use an approved existing group OU in a documentation namespace:
$path = 'OU=AccessGroups,DC=ad,DC=business,DC=example,DC=org'
New-ADGroup -Name 'GG-Reporting-Staff' -GroupScope Global `
    -GroupCategory Security -Path $path `
    -Description 'Approved ordinary reporting staff role'
New-ADGroup -Name 'DL-Reports-Modify' -GroupScope DomainLocal `
    -GroupCategory Security -Path $path `
    -Description 'Modify access to the approved reports resource'
Replace the path and names only after validating the design and uniqueness. Use security groups for access decisions; a distribution-only group is not interchangeable for permissions.
Keep descriptions useful but non-sensitive. Record the data owner, approver and review process in the authorised access register rather than embedding secrets or long policy text in the group.
Build the reviewed membership chain
$role = Get-ADGroup -Identity 'GG-Reporting-Staff'
$resource = Get-ADGroup -Identity 'DL-Reports-Modify'
Add-ADGroupMember -Identity $resource -Members $role
# Add only approved individual accounts to the role group.
Add-ADGroupMember -Identity $role -Members 'mreed'
The user name is illustrative. Resolve the intended principal and approval rather than selecting by a similar display name. Avoid circular or unnecessary deep nesting that makes effective access difficult to explain.
Assign the resource group its approved permission using the supported resource interface. Verify inheritance and existing denies before interpreting the effective result.
Test both entitlement and restriction
Use a representative ordinary account to open, create or modify only the intended information. Verify that another unrelated resource remains inaccessible. Test through the actual client path, including the SMB share where relevant.
Group changes may not immediately replace an existing user’s logon token or established session. Coordinate a supported fresh sign-in where needed rather than repeatedly editing ACLs while testing stale context.
Do not disable UAC or grant local administrator membership because a folder test fails. Inspect share permissions, NTFS inheritance, group scope and the actual account context separately.
Review the chain rather than a flat member list
Get-ADGroupMember -Identity 'GG-Reporting-Staff'
Get-ADGroupMember -Identity 'DL-Reports-Modify'
Get-ADGroupMember -Identity 'DL-Reports-Modify' -Recursive
Direct membership explains the design; recursive membership helps identify effective included principals. Keep both views for review, because a flattened list can hide which role created an entitlement.
At staff changes, update role membership. At resource changes, update the resource group’s permission design. This separation reduces repeated individual ACL edits and makes ownership easier to audit.
Reverse and retire with dependencies intact
If a grant was incorrect, remove the reviewed membership or permission that introduced it and verify active access through the approved revocation process. Consider existing sessions rather than assuming every token disappears immediately.
Before deleting a group, check resource ACLs, application configuration and nesting. Recreating the name creates a different SID and does not automatically restore old references.
See file-permission application and Microsoft’s security-group scope documentation for supported membership rules.
 Designing and promoting the first controller in a new AD forest
Prepare a new Active Directory forest with reviewed naming, functional levels and recovery. Install AD DS, run prerequisite checks, promote…
 Introducing an additional domain controller into a healthy directory
Introduce a writable controller only after directory health, functional compatibility and preparation rights are verified. Test promotion,…
 Creating protected organisational units with clear policy boundaries
Create an AD organisational unit for a defined delegation or policy purpose. Review inheritance, use a protected creation, verify placement…
 Provisioning an Active Directory user without exposing credentials
Provision an approved AD user through unique identifiers, a secure credential prompt and staged access review. Verify group membership,…
 Enabling AD Recycle Bin as an irreversible forest change
Plan AD Recycle Bin as an irreversible forest feature. Verify prerequisites, scope and replication, understand pre-existing deletion limits…
