Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Describe the client journey first
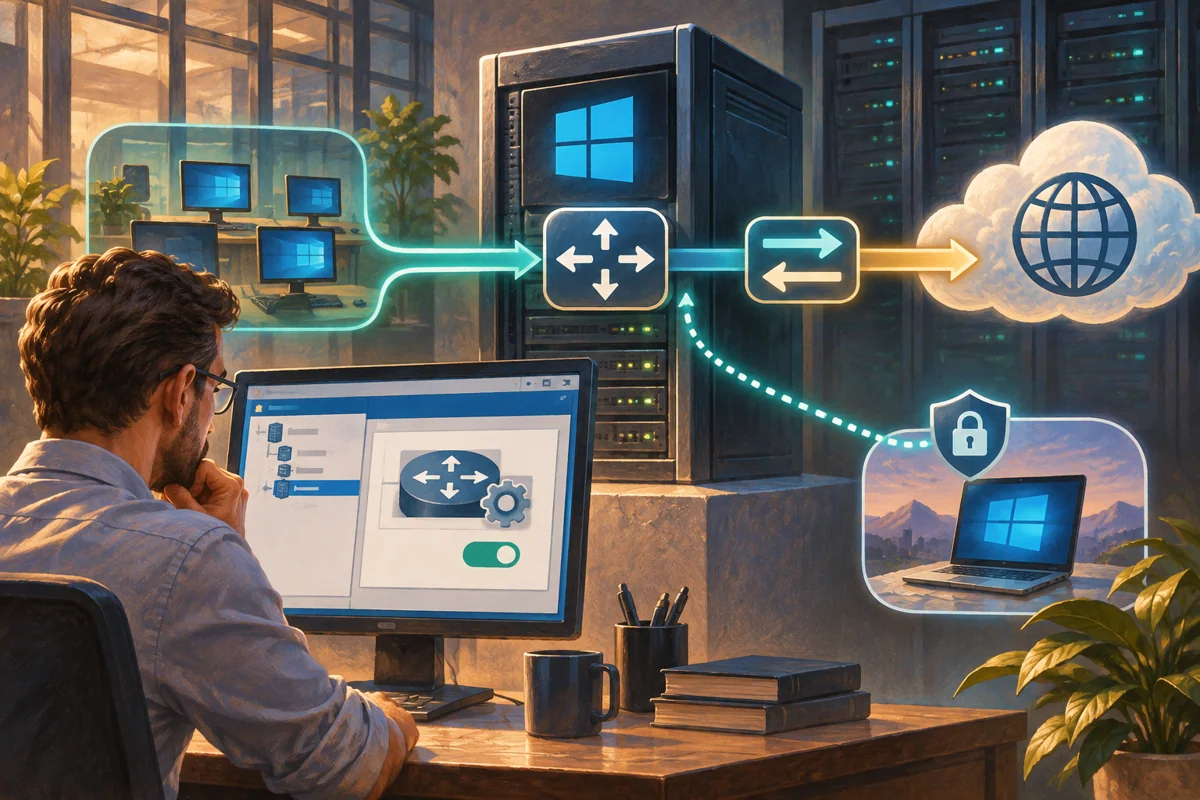
For outbound NAT, an internal client sends a connection to its gateway, the gateway translates the source address on the external path, and replies are matched back to that client. A problem anywhere in that journey can look like “NAT is broken”. Begin with a diagram or written route showing the client subnet, RRAS internal address, external interface, upstream gateway and DNS path.
Netcloud24 normally prepares that connectivity within an agreed managed deployment. The customer-facing requirement is working authorised access; the gateway’s NAT configuration is an infrastructure task. This procedure is for the administrator responsible for a traditional RRAS IPv4 NAT service, not for a customer to apply inside an ordinary VPS without confirming the provider’s routing model.
Keep RRAS NAT distinct from other translation services
Traditional RRAS NAT is configured in Routing and Remote Access. WinNAT, commonly administered through New-NetNat for virtual networks, is a separate mechanism. Internet Connection Sharing and software-defined-network translation are different again. Combining examples from those systems can leave overlapping state that is difficult to troubleshoot and unsupported for the intended path.
Use a server with the approved routing capability and two identified network sides. Microsoft’s RAS Gateway supports NAT44 in this context; an IPv6 translation requirement needs a different supported design. Confirm platform support, especially when the gateway is virtual, and verify upstream permission for forwarded traffic.
Define the internal range without overlap with remote sites, client VPN pools or upstream networks. Here 172.23.10.0/24 is illustrative and RRAS uses 172.23.10.1 internally. Replace those addresses after checking the complete network inventory. NAT does not make ambiguous overlapping routes safe.
Record the baseline and prepare the router
Keep console access available and record current routes and DNS settings before enabling forwarding. The external side normally has the planned upstream default route. Internal routes should match the private topology rather than adding unrelated default gateways to both NICs. A server-originated connection does not exercise the same path as forwarded client traffic.
Get-NetAdapter | Select-Object Name,ifIndex,MacAddress,Status
Get-NetIPConfiguration
Get-NetRoute -AddressFamily IPv4
Get-WindowsFeature Routing
Get-Service RemoteAccess -ErrorAction SilentlyContinue
For a new routing-only server, install Routing with management tools and initialise the intended mode. If RRAS already supports VPN users or another site, preserve its configuration and integrate the change rather than resetting it.
Install-WindowsFeature Routing -IncludeManagementTools
# Only for a new routing-only configuration:
Install-RemoteAccess -VpnType RoutingOnly
Read installation results and complete any required restart in a planned window. The service starting successfully establishes only one prerequisite for NAT.
Assign public and private NAT roles in the console
Open Routing and Remote Access and inspect IPv4. Add the NAT routing protocol through General if it is not already present. If a previous setup workflow created it, review its entries instead of duplicating them. Identify the external adapter from the recorded address and port mapping, not merely its friendly name.
Under NAT, add that interface as Public interface connected to the Internet and enable NAT for it. Public here is the RRAS translation role; it is not an instruction to change Windows network profiles or open every firewall service. Add the internal adapter as Private interface connected to private network, then review the pair together.
Leave address pools empty unless the design owns and routes additional external addresses. Leave service and port mappings empty unless an internal service has an approved publication requirement. An outbound-access task should not silently expose RDP or a web-management console. Capture the chosen interface roles and external source address in the change record.
Set one client’s next hop and resolver deliberately
Use a disposable or authorised pilot client in the internal range. Assign a valid unused address, correct mask and the intended DNS servers. Where RRAS is its default router, use the internal RRAS address as gateway. If another LAN router sits between the client and RRAS, configure the necessary route on that router instead of assuming every client should change gateway.
# On the internal pilot client:
Get-NetIPConfiguration
Get-NetRoute -AddressFamily IPv4
Test-NetConnection '172.23.10.1'
Resolve-DnsName 'www.microsoft.com'
Test-NetConnection 'www.microsoft.com' -Port 443 -InformationLevel Detailed
These checks answer different questions: reaching the gateway, resolving a name and establishing a TCP service connection. A failed ping can reflect ICMP filtering, so compare it with the actual service test. Test the intended application as well; port 443 working does not prove an unrelated application protocol is allowed.
Observe translation and prove the exposure boundary
While the client makes an approved outbound request, inspect RRAS NAT mappings and statistics on the external interface. Confirm the observed connection belongs to the pilot’s address and reaches the intended destination. Do not use only a browser on the gateway as evidence that client forwarding works.
Check the return path and filtering on the upstream device. From an authorised external test point, verify that internal services remain unpublished unless a separate mapping and rule intentionally permit them. NAT is a translation mechanism, not a complete substitute for a firewall policy. Keep Windows Firewall, RRAS filters and upstream controls aligned with the actual allowed flows.
If inbound publication is later needed, treat it as another change specifying protocol, external port, internal host and source scope. Review certificate and application authentication requirements too. A working translation does not establish that the exposed application is safe.
Follow the evidence when clients still fail
If the internal gateway is unreachable, inspect the client mask, VLAN and local network before editing NAT. If the gateway is reachable but all external TCP tests fail, inspect the external route, interface roles, provider forwarding and firewall policy. If IP access works while names fail, examine the resolver path and DNS rules.
For intermittent stalls, correlate the connection with packet loss, gateway capacity, asymmetric routes and MTU behaviour. Small probes can work when larger packets fail. Record source, destination, protocol, port and time so the upstream team can match its evidence. Do not add WinNAT or enable Internet Connection Sharing as an improvised repair to a traditional RRAS deployment.
Remove a pilot without breaking established traffic
Rollback begins with dependency review. Remove only the newly introduced NAT mappings or interface entries, restore the pilot client’s recorded gateway settings and verify the previous path. Disabling all RRAS can disconnect remote-access users or site links unrelated to the NAT task. Global address-pool or port changes may affect other clients as well.
Retain logs and configuration until the change is accepted or the incident is understood. Document the client networks, interface identities, external address, upstream route, DNS dependency and security owner. Monitor the gateway as a shared service: many healthy client NICs can still depend on one failed translation boundary.
 Preparing RRAS for an agreed Windows Server gateway role
Prepare RRAS by choosing its gateway purpose, verifying platform support and interface design, installing only needed services, and testing…
 Building a certificate-validated IKEv2 remote-access service
Design an IKEv2 service around gateway and EAP certificate validation, narrow NPS authorisation, managed client provisioning and external…
 Connecting two routed sites through an RRAS IKEv2 interface
Connect two sites using an RRAS IKEv2 interface with machine certificates, complementary subnet routes and matched responder policy, then…
 Introducing NPS as a controlled RADIUS authority
Introduce NPS with distinct AD registration and RADIUS peer trust, narrow policy matching, current integrity and certificate requirements,…
 Maintaining a specific Windows Server route without changing the default path
Maintain a subnet-specific Windows route with a verified interface and next hop, prove source selection and application reachability, and…
