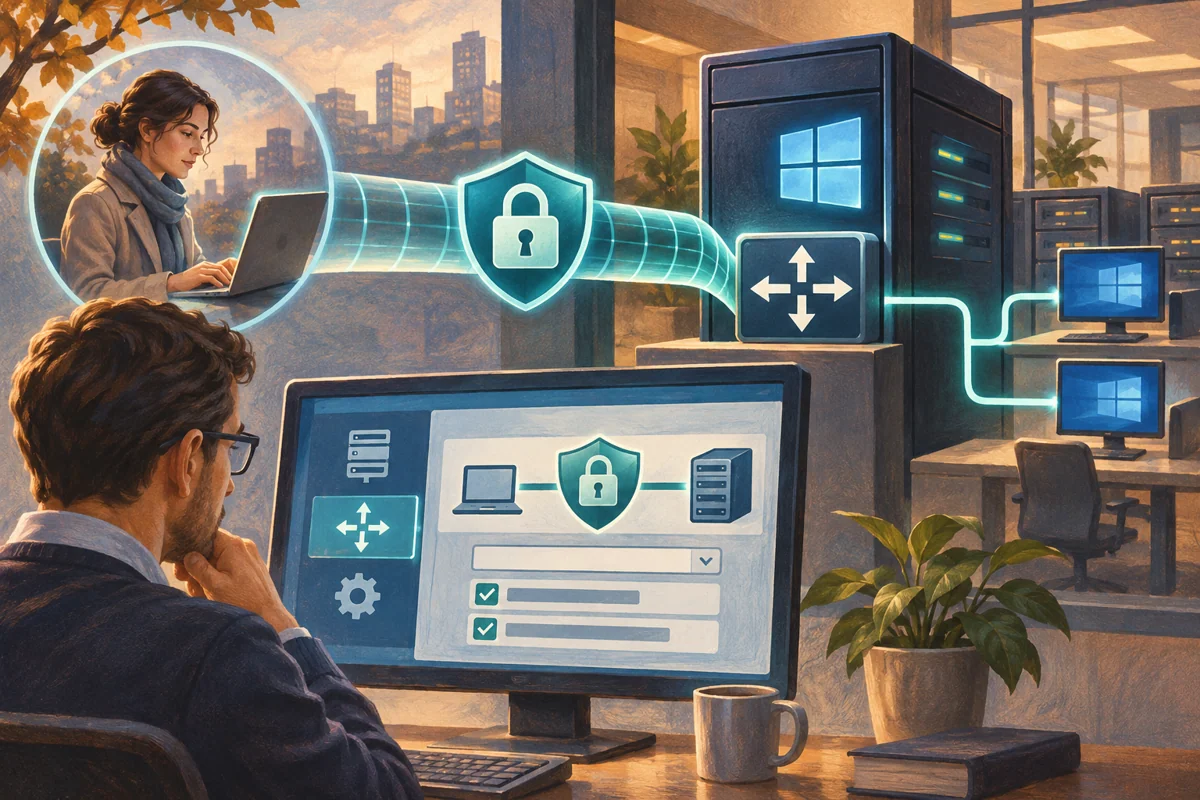
Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Treat identity validation as part of the connection
An IKEv2 tunnel can encrypt traffic while the overall access service is still poorly controlled. The deployment must establish which gateway the client trusts, which user or device is allowed to authenticate, and which internal resources that identity may reach. Start with those decisions rather than a protocol dropdown. This article uses an RRAS IKEv2 endpoint with EAP-TLS user authentication through NPS.
In a managed Netcloud24 environment, the team prepares the gateway, policy, certificates and client settings within the agreed service. The customer should receive usable access and a support process, not responsibility for assembling a PKI. The steps below explain the authorised administrator’s design and verification work. They do not describe a device tunnel or a site-to-site interface, which have different identity and routing requirements.
Prepare three distinct certificate responsibilities
The VPN gateway needs a machine certificate for the IKEv2 endpoint, with the expected public name, private key and required purposes. In Microsoft’s documented design, check Server Authentication and IP security IKE intermediate requirements. Clients must trust its issuing chain and verify the endpoint name, such as access.corp.example. A private internal server name is not interchangeable with the public name users connect to.
NPS needs its own appropriate server-authentication certificate for the EAP exchange. The user needs a client-authentication certificate and private key that maps correctly to the authorised AD account. These responsibilities can share a PKI, but they are not one undifferentiated “VPN certificate”. Confirm stores, purposes, identities, expiry and renewal for each.
Make revocation information reachable before the tunnel exists. A client that needs the VPN to fetch the gateway’s CRL can fail during bootstrap. For AD-backed authentication, current domain-controller strong mapping requirements also matter: a plausible UPN alone is not proof of a strong certificate-to-account binding. Correct issuance or an approved strong mapping is preferable to obsolete compatibility-registry workarounds.
Design the network and supported gateway platform
Choose a public DNS endpoint, a non-overlapping client pool, internal DNS and a return route from the corporate network to that pool. Avoid address ranges commonly used by home networks where practical, and document unavoidable overlap handling. Decide split-tunnel or full-tunnel behaviour and enforce resource access separately from basic VPN connectivity.
Confirm the Windows Server Remote Access deployment is supported on the hosting platform. Microsoft excludes this role’s deployment in Azure VMs; another platform requires its own forwarding and IPsec support review. Plan UDP 500 and 4500, NAT traversal and applicable upstream controls. A TCP probe on those numeric ports does not validate IKEv2.
Get-NetIPConfiguration
Get-NetRoute -AddressFamily IPv4
Get-ChildItem Cert:\LocalMachine\My |
  Select-Object Subject,Thumbprint,NotAfter,HasPrivateKey
Install-WindowsFeature DirectAccess-VPN -IncludeManagementTools
Bring up only the approved RRAS VPN function
For a new server, use the VPN-only Remote Access workflow, then the RRAS custom configuration for VPN access. Preserve existing configuration if the server already serves another purpose. In IPv4 settings, configure the reserved static client-address pool or the deliberately designed alternative assignment method. Review the corresponding internal return routes before accepting client traffic.
In Ports properties, enable the intended IKEv2 remote-access capacity and disable unused protocol acceptance. New Windows Server 2025 installations differ from historical defaults for PPTP and L2TP, while upgraded configurations can retain earlier behaviour. Inspect the actual port settings on every release. Do not enable weak fallback protocols because an IKEv2 pilot has not yet connected.
If custom IPsec policy is required by the security baseline, select modern compatible transforms and configure the matching client policy. Keep those choices documented. Copying old DH groups from a compatibility example can create an unrelated downgrade without explaining the original negotiation failure.
Authorise a narrow pilot through NPS
Install and register NPS with the necessary directory permissions. Where it is separate from RRAS, define the gateway as a known RADIUS client using the source address NPS actually sees, a protected strong secret and limited firewall scope. Set RRAS to the intended RADIUS authentication and accounting peer. Local NPS is a different topology and does not need a fictional external client relationship.
Create a policy for a small approved group and the VPN access scenario. Use the certificate EAP method and select the intended NPS certificate. Check connection-request policy and network-policy order so an earlier broad policy cannot accept the login through a different method. Remove unapproved methods rather than allowing everything during the pilot.
Retain authentication and accounting evidence with appropriate access and retention. RRAS and NPS alone do not automatically supply MFA. If the service requires it, use a separately supported authentication design rather than describing EAP-TLS as a universal substitute for every access requirement.
Distribute a profile that verifies expected servers
Provision the Windows client profile through the approved management process. Specify the endpoint name, IKEv2 and the certificate EAP method. Configure validation of the expected EAP server names and trusted roots; do not leave users to approve an arbitrary authentication certificate in a prompt. Install the required user certificate and chain securely.
# Inspect the pilot client without displaying private material:
Get-VpnConnection -Name 'Managed Access'
Get-ChildItem Cert:\CurrentUser\My |
  Select-Object Subject,NotAfter,HasPrivateKey
# After a connection attempt:
Get-NetIPConfiguration
Get-NetRoute -AddressFamily IPv4
Inspect the assigned VPN address, routes, DNS servers and suffix behaviour after connection. Verify the traffic intended for the tunnel actually uses it. A Connected label does not demonstrate that a database request follows the protected route or that unapproved internal networks remain blocked.
Prove acceptance and rejection from outside
Use a genuinely external client network and an authorised pilot user with a valid certificate. Check connection, internal name resolution and specific application access. Then test an out-of-group account or missing suitable certificate and confirm rejection. Use disposable test identities and avoid repeated failures that trigger account lockout.
Correlate the client’s RasClient/IKE evidence with RRAS and NPS records, including the selected policy and denial reason where auditing is enabled. If the tunnel forms but resources fail, focus on routes, return paths, DNS and resource firewalls. If it fails before authentication, examine transport, negotiation and gateway certificate validation. Preserve exact codes and times.
Keep troubleshooting and renewal within the security model
For certificate problems, inspect SAN, purposes, key availability, chain, mapping, expiry and revocation reachability. For NPS denial, investigate the actual matched policy rather than broadening every condition. For transport failure, inspect UDP/IPsec handling and upstream restrictions. Do not turn off validation, enable PPTP or bypass revocation as a routine test.
Rollback the pilot profile and only its introduced gateway or policy changes while preserving logs. Document endpoint ownership, address pool, return routes, certificate renewal and revocation response. Recheck both successful and rejected access after client or Windows Server upgrades. The managed outcome is an access service whose trust and routing remain understood throughout its lifecycle.
 Preparing RRAS for an agreed Windows Server gateway role
Prepare RRAS by choosing its gateway purpose, verifying platform support and interface design, installing only needed services, and testing…
 Providing controlled outbound IPv4 access with RRAS NAT
Configure traditional RRAS outbound NAT from the client’s full route, assign deliberate interface roles, verify actual translations and…
 Connecting two routed sites through an RRAS IKEv2 interface
Connect two sites using an RRAS IKEv2 interface with machine certificates, complementary subnet routes and matched responder policy, then…
 Introducing NPS as a controlled RADIUS authority
Introduce NPS with distinct AD registration and RADIUS peer trust, narrow policy matching, current integrity and certificate requirements,…
 Maintaining a specific Windows Server route without changing the default path
Maintain a subnet-specific Windows route with a verified interface and next hop, prove source selection and application reachability, and…
