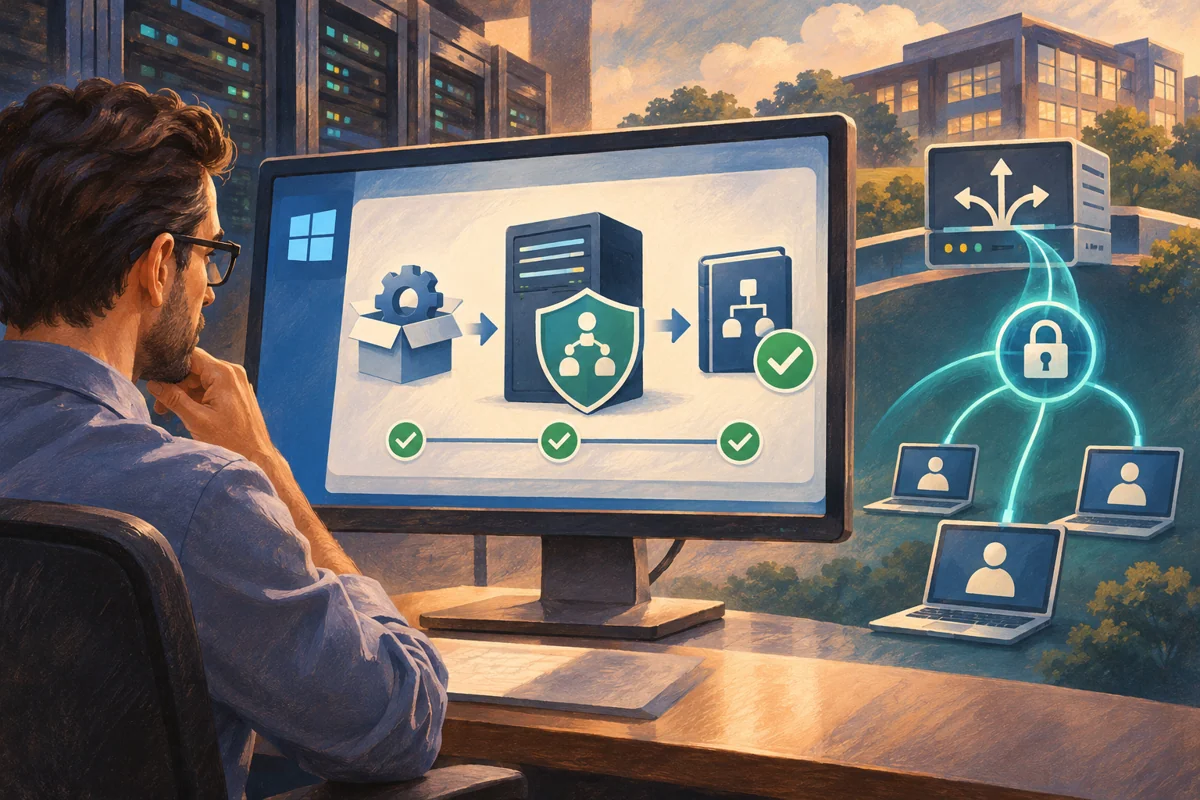
Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Distinguish the people, devices and directory permissions
Network Policy Server evaluates RADIUS requests from VPN gateways, wireless controllers, switches or other known access devices. Those devices are RADIUS clients; the employee’s laptop is usually the endpoint authenticating through them. Separately, an AD-integrated NPS computer needs permission to read relevant directory account properties. Keeping those relationships distinct prevents a common installation mistake: registering NPS in AD and assuming every access device is now authorised to send it requests.
In a managed Netcloud24 environment, the service team prepares the NPS host, peer configuration and policy as part of the access design. The customer should have an agreed authentication service and support route, not a requirement to administer RADIUS. This guide describes the authorised administrator’s introduction of one controlled NPS instance.
Define the authority and availability model
Decide whether NPS processes requests locally, proxies them to another authority, or does both through distinct connection-request policies. Inventory the access devices and their actual source addresses, authentication and accounting ports, vendor settings and secret owners. A gateway behind NAT may reach NPS from a different address than its management interface.
Plan more than installation capacity. A single NPS can become a shared dependency for VPN, office Wi-Fi and switch access. Define redundancy and the access devices’ failover behaviour before the first server is treated as critical. Keep DNS, time and domain connectivity dependable; AD-based authentication depends on them.
Protect the RADIUS network path and restrict listeners to the approved peers. A shared secret does not make UDP RADIUS equivalent to an encrypted general-purpose tunnel. Current Message-Authenticator guidance and client compatibility belong in the rollout, together with secure credential handling and log retention.
Install and inspect the Windows service
Use elevated Windows PowerShell on a patched domain-member server with an appropriate administrative installation identity. Inspect the feature before adding it, then review the result and any restart requirement. The service name is IAS, which differs from the product name shown in the console.
Get-WindowsFeature NPAS
$setup = Install-WindowsFeature NPAS -IncludeManagementTools
$setup | Format-List Success,RestartNeeded,ExitCode
Get-Service IAS
Get-NetConnectionProfile
Resolve an unexpected domain-network profile or DNS issue before making this server an authentication dependency. Installation provides the console and service; it does not create an application-specific policy or validate a single real login. Preserve the initial configuration and record the intended role as local authority or proxy.
Grant directory access through the proper registration
In the NPS console, register the local NPS server in Active Directory using an account authorised to make the directory change. Registration adds the computer account to the RAS and IAS Servers group. It is the server’s computer identity that needs membership, not the currently signed-in administrator.
# From an approved AD administration system:
Get-ADGroupMember 'RAS and IAS Servers' |
  Select-Object Name,ObjectClass,SamAccountName
Get-ADComputer 'AUTH01' -Properties DNSHostName |
  Select-Object Name,DNSHostName,Enabled
Verify the intended account appears and allow for directory replication and relevant token refresh. If users reside in another domain, evaluate its registration and trust requirements explicitly. Local-domain registration is not a universal cross-domain permission grant. A denied registration should lead to checking delegation and target domain rather than giving the service broad domain-administration rights.
Create an authenticated relationship with each access device
Add the known gateway or controller under RADIUS Clients and Servers with a descriptive name, verified source address and strong protected shared secret. Configure the same secret and peer details on that device through its approved management interface. Avoid displaying secrets in tickets, screenshots or PowerShell transcripts.
Review active UDP listeners and firewall scope. Common modern ports are 1812 for authentication and 1813 for accounting; NPS can also listen on legacy ports. Retain only the ports required by the actual devices and restrict their sources. A TCP reachability result does not prove that an Access-Request reached the UDP listener.
Follow Microsoft’s RADIUS hardening guidance for Message-Authenticator, including requests, proxy behaviour and responses where applicable. Test each peer’s support before enforcement rollout. If a request is dropped, inspect update levels and attribute behaviour; turning off integrity checks globally is not an appropriate first fix for an old access device.
Build a small policy whose success is meaningful
Use a limited AD pilot group and a condition matching the intended access scenario. Review connection-request policy first because it decides local processing versus forwarding. Then inspect network-policy order and constraints. An earlier broad policy can accept a request before the carefully scoped pilot policy is considered.
Choose the approved authentication method. For EAP-TLS or PEAP, select the correct NPS certificate and ensure the endpoint verifies expected server names and roots. Certificate clients also need suitable certificates, private keys and account mapping. AD-backed certificate authentication must satisfy current strong-mapping enforcement; a weak name-only assumption from an old guide may now fail.
Do not enable extra password methods or all-user conditions simply to obtain a grant event. Configure authentication and accounting logging with protected retention and capacity monitoring. Decide how accounting failures affect access, because full log storage can become an availability issue as well as an evidence gap.
Generate one authorised request and one deliberate denial
Test through the actual access device and client path. An authorised pilot should be granted by the intended policy and method. An out-of-group identity or unsuitable credential should be denied. Keep test attempts controlled to avoid account lockout and use non-production credentials where feasible.
# Where NPS success and failure auditing is enabled:
Get-WinEvent -FilterHashtable @{
  LogName='Security';Id=6272,6273;StartTime=(Get-Date).AddHours(-1)
} -MaxEvents 30
Get-WinEvent -FilterHashtable @{
  LogName='System';ProviderName='NPS';StartTime=(Get-Date).AddHours(-1)
} -MaxEvents 30
Record the policy, reason, device source and authentication method rather than only “login worked”. If no event appears, check auditing and packet arrival before assuming the user password is wrong. Review accounting separately: a grant does not prove the accounting record reached its destination.
Diagnose and maintain the authority deliberately
For unknown clients or dropped packets, check source address, UDP path, secret agreement and Message-Authenticator behaviour. For a processed rejection, use the recorded reason to inspect policy order, group membership, dial-in permissions, certificate mapping or the selected EAP method. Cross-domain failures need trust, DNS and directory-access checks as well.
Rollback only the new pilot policy and client entries while preserving logs. Before retiring NPS, move every access device to another verified authority and review directory membership cleanup. Keep certificate renewal, shared-secret rotation, policy ownership and recovery documented. The operational goal is understandable and auditable acceptance and rejection, not a service process that merely remains Running.
 Preparing RRAS for an agreed Windows Server gateway role
Prepare RRAS by choosing its gateway purpose, verifying platform support and interface design, installing only needed services, and testing…
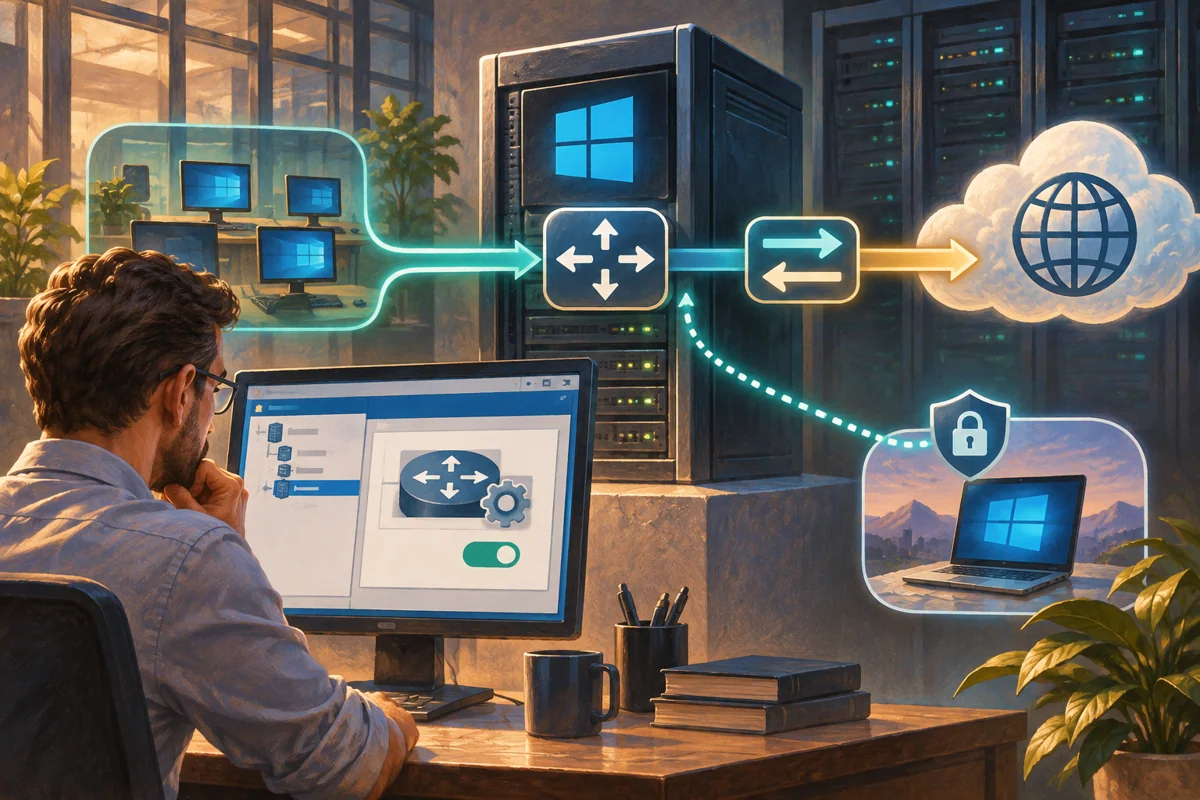 Providing controlled outbound IPv4 access with RRAS NAT
Configure traditional RRAS outbound NAT from the client’s full route, assign deliberate interface roles, verify actual translations and…
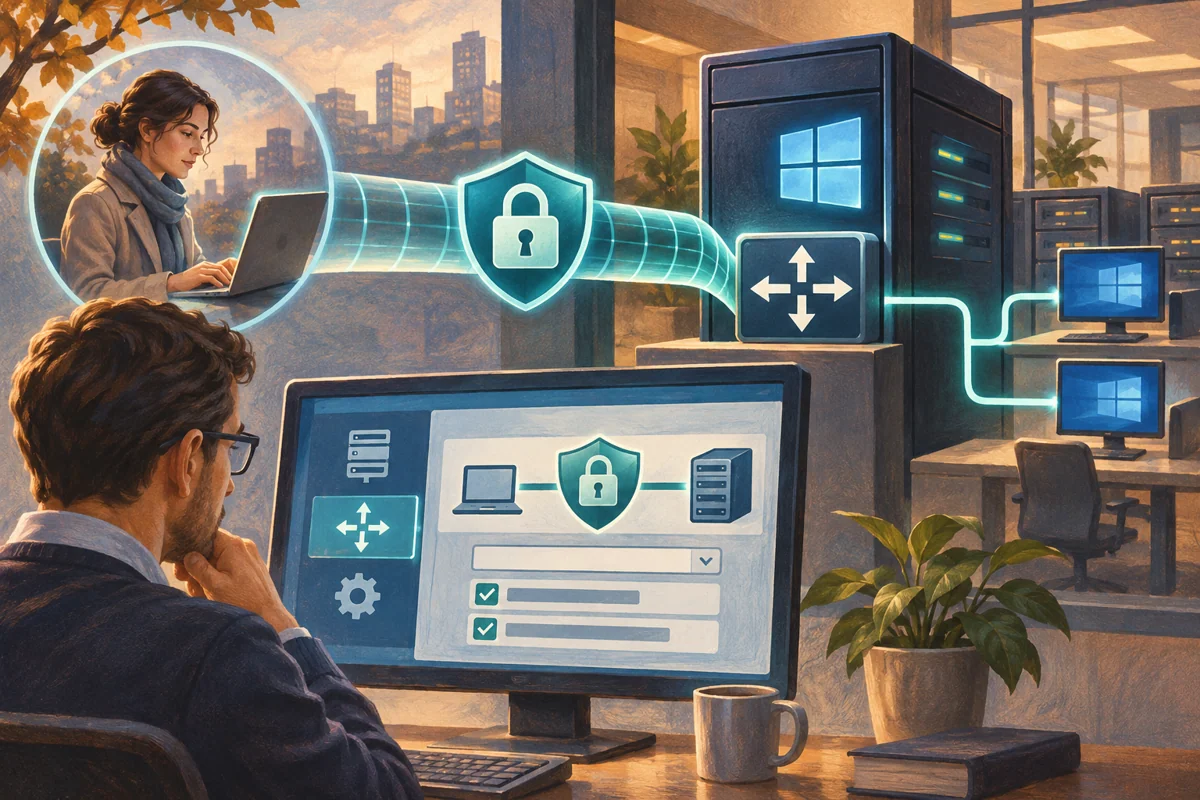 Building a certificate-validated IKEv2 remote-access service
Design an IKEv2 service around gateway and EAP certificate validation, narrow NPS authorisation, managed client provisioning and external…
 Connecting two routed sites through an RRAS IKEv2 interface
Connect two sites using an RRAS IKEv2 interface with machine certificates, complementary subnet routes and matched responder policy, then…
 Maintaining a specific Windows Server route without changing the default path
Maintain a subnet-specific Windows route with a verified interface and next hop, prove source selection and application reachability, and…
