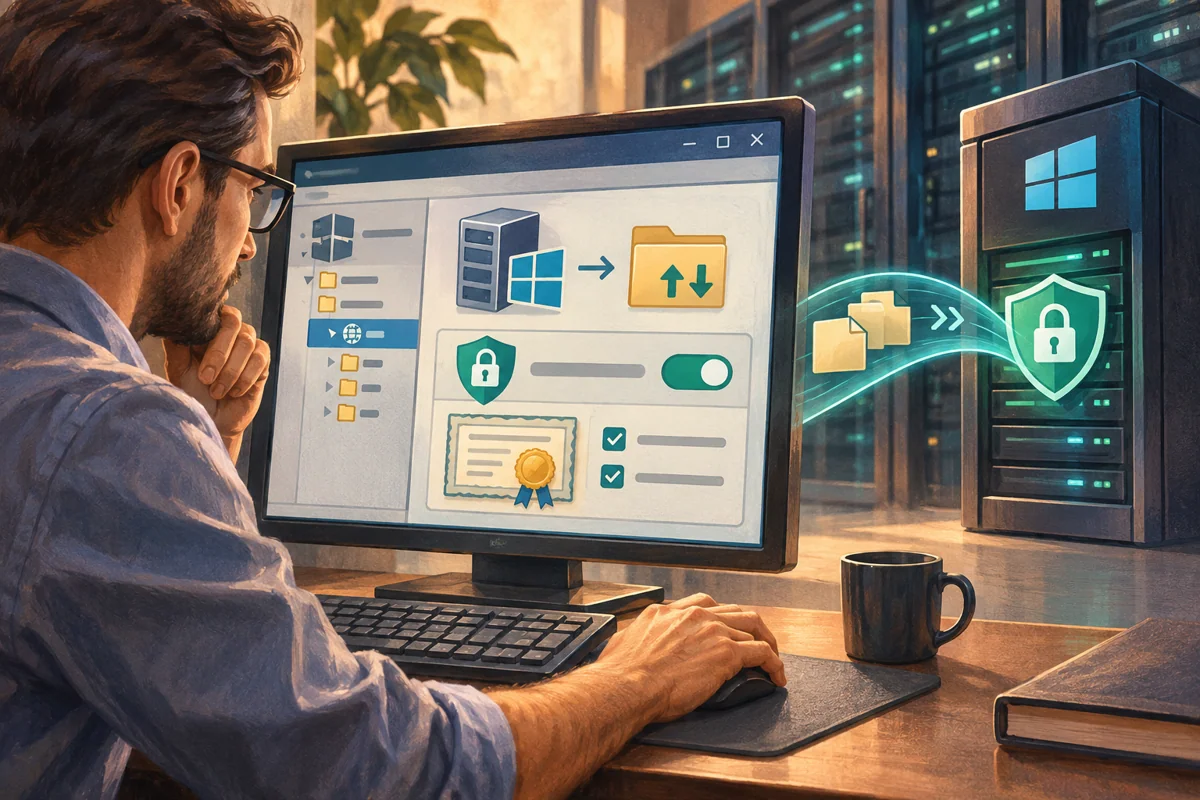
Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Agree FTPS rather than an ambiguous “secure FTP” requirement
FTPS and SFTP are different protocols. IIS FTP can protect its FTP control and data connections using TLS; SFTP normally belongs to an SSH service and uses a different client mode and port. Confirm the partner’s actual protocol before opening a firewall or issuing credentials. This guide uses explicit FTPS on port 21, with TLS required for the whole transfer.
For managed Netcloud24 delivery, the team prepares the endpoint, certificate, account scope and network path. Customers or partners receive the agreed connection details rather than a requirement to configure the Windows FTP service. The following is the administrator’s build and acceptance workflow, including the data connection that a simple login test often misses.
Set access and storage boundaries before creating the site
Decide whether the partner may download, upload, rename or delete files. Grant the smallest required NTFS and FTP authorisation rights. Modify is broader than upload-only because it includes normal editing and deletion. If unrelated users must never see each other’s content, select a supported user-isolation model and matching directory structure, not merely different folder names beneath one shared root.
Reserve a service name such as exchange.corp.example and obtain a certificate whose SAN matches it and whose chain the actual clients trust. Check Server Authentication purpose, expiry, private key and revocation reachability. An internal CA is not automatically trusted by an external partner. Protect certificate import material and keep renewal ownership clear.
Choose a bounded passive data range, for example 51000–51080, sized for intended concurrency. Record every firewall and NAT hop. Explicit FTPS can authenticate successfully while listings and uploads stall because the separate passive connection cannot reach the advertised address and port.
Install the FTP components and review directory access
Install the FTP role service on the approved server and inspect service state. Do not assume the IIS web role alone supplied FTP. Create the reviewed new transfer directory without silently reusing existing content, then apply the partner group’s agreed permissions.
Install-WindowsFeature Web-Ftp-Server -IncludeManagementTools
Get-WindowsFeature Web-Ftp-*
Get-Service ftpsvc
New-Item -ItemType Directory -Path 'E:\Exchange\Supplier-One' -ErrorAction Stop | Out-Null
icacls 'E:\Exchange\Supplier-One' /grant:r 'CORP\DL-SupplierOne-Transfer:(OI)(CI)M'
icacls 'E:\Exchange\Supplier-One'
The example assumes a read/write/delete agreement for that group; change it for a narrower workflow. Review inherited access, ownership and system/administrator recovery rights. Keep inbound transfer data away from executable website content. A partner account should not be able to replace the code of another service simply because it can upload files.
Create the explicit-TLS site with named access
In IIS Manager, add the FTP site with its intended physical path, local address and port 21. Select the approved certificate and Require SSL. Disable anonymous authentication and enable the agreed named-account method. With Basic Authentication, mandatory TLS must protect credentials before they are sent; ordinary unprotected FTP exposes them.
Allow only the approved users or group in FTP Authorisation Rules, with the required operations. Check the advanced SSL channel policies after creation: require TLS on control and data. “Allow SSL” and “require credentials only” are weaker policies because they can permit unprotected portions of the session. Do not select those modes to accommodate a client that was configured incorrectly.
Keep the endpoint stopped or network-restricted until trust, permissions and passive networking are ready. Do not add an implicit FTPS listener as an undocumented alternative. If that is the partner’s requirement, create and verify the corresponding explicit design rather than mixing client modes during troubleshooting.
Align passive ports with the external address
The passive data range is a server-level FTP setting and can affect other FTP sites. Review existing use before changing it. Configure the agreed range through FTP Firewall Support or the supported configuration commands, then arrange any required service restart in a maintenance window.
Import-Module WebAdministration
Set-WebConfigurationProperty -PSPath 'MACHINE/WEBROOT/APPHOST' `
  -Filter 'system.ftpServer/firewallSupport' -Name lowDataChannelPort -Value 51000
Set-WebConfigurationProperty -PSPath 'MACHINE/WEBROOT/APPHOST' `
  -Filter 'system.ftpServer/firewallSupport' -Name highDataChannelPort -Value 51080
For a NATed service, set the relevant site’s advertised external IPv4 address to the address the client must reach. Forward TCP 21 and the selected passive ports to the server and apply source restrictions where feasible. An encrypted control session cannot be parsed by every legacy FTP inspection helper, so use an FTPS-compatible firewall policy. Do not open every high port as a substitute for matching the configured range.
Accept the service through a complete external transfer
Use an approved client in explicit-TLS mode, validate the endpoint certificate and test from the partner’s real network or a representative authorised external path. A localhost test bypasses much of the NAT and firewall chain. Do not accept an unexpected certificate solely because the next screen asks for a password.
Verify login, directory listing and every authorised file operation using disposable content. Compare the transferred content or hash, then remove the test artifact through the agreed workflow. Test an unapproved identity and confirm rejection. Verify that a cleartext session cannot perform the protected workflow and that the data channel remains encrypted.
Get-NetTCPConnection -State Listen -LocalPort 21
Get-Website | Select-Object Name,Id,State,PhysicalPath,Bindings
Test-NetConnection 'exchange.corp.example' -Port 21
These server and TCP checks support the full client test; they do not replace it. Inspect the correct site’s FTP logs, allowing for buffering, and protect records containing usernames and file paths. Never share a client transcript that reveals credentials.
Use the failure stage to guide diagnosis
A TLS handshake failure leads to certificate identity, trust, key and protocol checks. A post-TLS login failure leads to account state, username format, authorisation and isolation requirements. A login that works but cannot list or transfer leads to passive ports, advertised address, NAT and client mode. A 550-style error can indicate file/path access rather than a broken network.
Correlate client timestamps and test filenames with FTP status, substatus and Win32 status. Do not enable anonymous access or relax data-channel encryption to make a single test succeed. Those changes alter the service’s security requirement rather than explain its fault.
Operate and withdraw access deliberately
Monitor failed logins, transfer storage, logs and certificate expiry. Define inbound malware handling, retention and partner offboarding. Keep the user-isolation and directory model documented so a later account addition does not expose another partner’s data.
Rollback a pilot by stopping its site and reversing only introduced rules and mappings after checking shared dependencies. Restoring the global passive range or restarting ftpsvc affects other sites too. Preserve uploaded data and evidence before deleting folders or accounts. The completed managed service is a protected and observable transfer path whose access and renewal remain owned throughout the relationship.
 Preparing IIS for the application rather than installing every feature
Prepare IIS from the application’s runtime and exposure requirements, inspect installed modules, verify controlled requests and logs, and…
 Building an IIS site with its own worker-process boundary
Build a dedicated IIS site and pool with deliberate runtime and anonymous identity, read-only code access and a unique staging response,…
 Publishing the correct HTTPS identity from IIS
Publish an IIS HTTPS hostname by identifying TLS termination, validating the exact certificate and key, checking SNI and HTTP.sys state,…
 Giving an IIS application a dedicated Windows runtime identity
Assign a justified dedicated IIS identity by tracing the effective access context, preparing narrow permissions, protecting credential…
 Using AppCmd as one part of an IIS recovery plan
Use named AppCmd backups for controlled IIS configuration rollback while protecting content, data, keys and runtimes separately, then…
