Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Define the two tiers and their operational owners
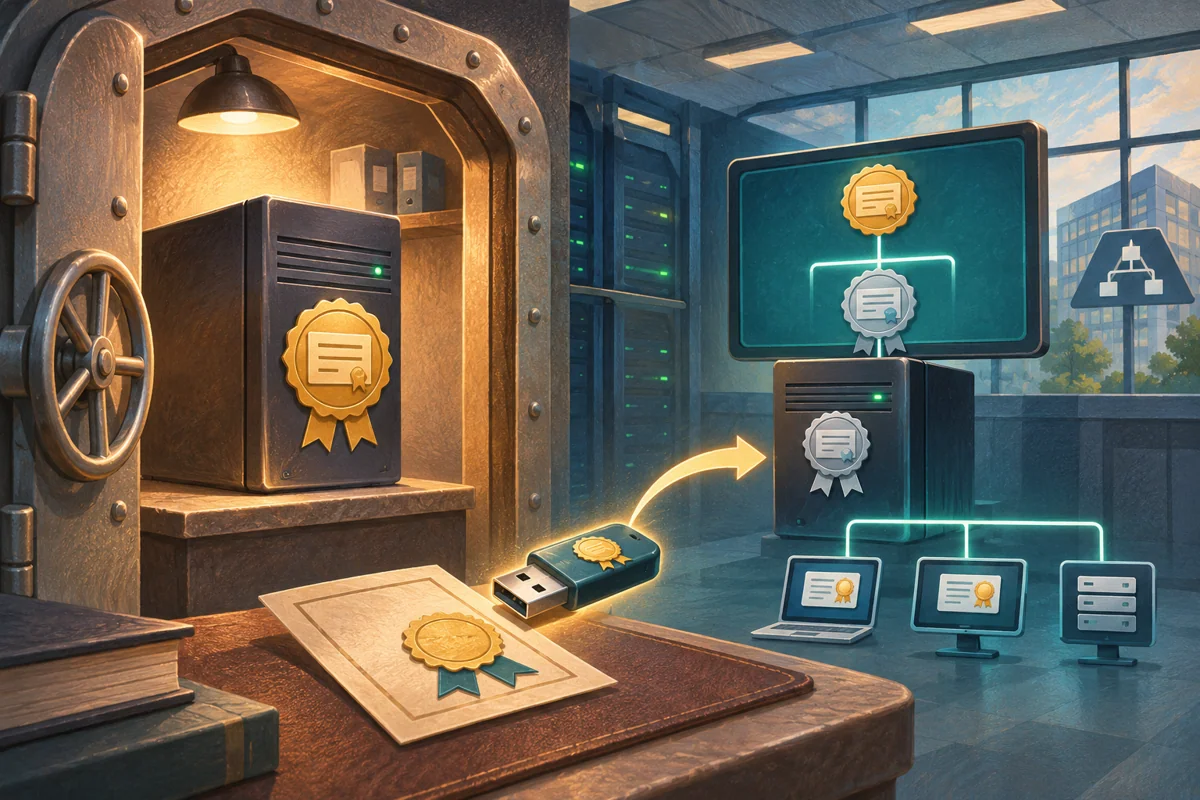
In a two-tier PKI, the root CA signs the issuing CA’s certificate and publishes root revocation information. The issuing CA handles routine certificate requests. Keeping the root offline reduces its network exposure, but creates an operational obligation: authorised staff must bring it up, verify its state, publish fresh material and return it to protected storage on schedule.
Netcloud24 can prepare the agreed hierarchy and managed issuing environment. The organisation still needs named trust and recovery owners, including custody of offline keys and authorisation to sign a subordinate request. This guide describes building the standalone root and completing that controlled signing boundary. It does not treat “offline” as a checkbox that removes maintenance responsibilities.
Set the publication and lifecycle design first
Choose stable root and issuing CA names, cryptography, validity, key protection, hierarchy depth and renewal plans. The root’s certificate must outlive the intended subordinate lifetime with adequate operational margin, but excessively long periods are not automatically better. Choose values from policy and relying-system support rather than a tutorial’s sample dates.
Plan a reachable publication service for the root certificate and CRL. The root itself remains offline; another system serves public verification material. The issuing CA certificate embeds the root CRL retrieval path, so that address must remain available for its supported lifetime. An expired root CRL can disrupt validation even though the root certificate remains valid.
Set a publication interval and overlap that the offline operating schedule can reliably meet. Define emergency publication for a subordinate-key compromise, not just routine calendar renewal. Decide how media is checked, approved, tracked and sanitised between the offline host and publication systems. Only required public material and reviewed requests should cross that boundary.
Prepare a standalone root host
Use a dedicated workgroup server, with the approved OS build and no routine network connection. Complete necessary preparation under the security process, then establish the offline boundary. Protect console access, storage, timekeeping and recovery media. A root left as an ordinary domain member and merely unplugged temporarily is a different trust model.
Place the role-specific reviewed CAPolicy.inf in the Windows directory before configuring AD CS. It influences relevant installation and renewal behaviour, and later edits do not retroactively rewrite existing certificates. Do not copy issuing-CA settings indiscriminately onto the root. Confirm the provider and any HSM recovery process before generating the root key.
Get-ComputerInfo | Select-Object CsName,WindowsProductName,OsBuildNumber,CsDomain
Get-Volume | Select-Object DriveLetter,FileSystemLabel,SizeRemaining,Size
Test-Path (Join-Path $env:windir 'CAPolicy.inf')
Install-WindowsFeature ADCS-Cert-Authority -IncludeManagementTools
Record the build and chosen identity outside the host. A future replacement must recover the original CA identity, not create an unrelated self-signed certificate with the same display name.
Create the standalone root deliberately
The following uses illustrative RSA and validity values. Confirm them against the hierarchy design and client compatibility. A standalone root does not integrate with AD template-driven enrollment, which is one reason it suits this limited offline function.
$offlineRoot = @{
  CAType = 'StandaloneRootCA'
  CACommonName = 'Example Offline Trust Root'
  CryptoProviderName = 'RSA#Microsoft Software Key Storage Provider'
  KeyLength = 4096
  HashAlgorithmName = 'SHA256'
  ValidityPeriod = 'Years'
  ValidityPeriodUnits = 18
}
Install-AdcsCertificationAuthority @offlineRoot
Get-Service CertSvc
Do not suppress or bypass a key/database conflict with overwrite options. Preserve evidence and investigate prior state. After installation, inspect the root certificate’s subject, public key, signature, validity and constraints. A successful installation message does not prove the hierarchy’s publication or recovery design is complete.
Configure and export public verification material
Review the root CA’s CDP/AIA configuration and publication timing before signing the issuing request. A self-signed root and a subordinate have different extension roles; use the reviewed hierarchy design rather than assuming the defaults fit both. Produce the initial CRL and export the root certificate to an approved transfer location.
certutil -getreg CA\CRLPublicationURLs
certutil -getreg CA\CACertPublicationURLs
certutil -CRL
# Use an existing controlled transfer directory:
certutil -ca.cert 'C:\PKI-Transfer\OfflineRoot.cer'
Inspect the generated CRL’s issuer, signature, this-update and next-update dates. Transfer only the approved public files through the controlled media process to the publication service. Test retrieval and validation from representative relying networks. The root generating a file locally is not proof that clients can retrieve the fresh version.
Review and sign the issuing CA request
On the separate domain-member issuing server, configure an EnterpriseSubordinateCA with its reviewed policy and generate the request for offline signing. Transfer that request to the root using the approved process. Before submission, inspect the requested identity, public key and extensions and compare the request’s provenance with the authorised issuing server.
Use the root’s Certification Authority management workflow to submit the reviewed request. A standalone CA commonly leaves it pending for approval. Inspect the pending request and issue only the intended subordinate certificate, with CA constraints and validity consistent with the hierarchy. Do not approve every pending item or turn the root into a routine end-entity issuer.
Export the signed subordinate certificate and required public chain, transfer them back and complete the issuing CA configuration. Verify its chain, CA purposes, embedded root revocation path and effective validity before allowing leaf issuance. Keep request and issuance identifiers with the approval record; the offline ceremony should be reconstructable later.
Prove the hierarchy before routine enrollment begins
From the issuing server and a representative client, validate the chain and fetch the root CRL through its actual advertised URL. Then issue a disposable permitted leaf certificate and verify its issuer and revocation path. The root and issuing CRLs serve different levels of the chain and need separate monitoring.
Protect the root key, database, configuration and ceremony records through a supported offline backup process. Test isolated restoration under controlled conditions and document custody. HSM and software-key backups have different recovery mechanics. A copy of the public root certificate cannot recover the signing key.
Return offline and keep the schedule real
Stop the root’s operational activity, secure the host and transfer media, and record the next required publication or renewal date. Monitor the served root CRL externally so a missed ceremony is detected before expiry. Keep an emergency route for revoking a compromised issuing CA and publishing that decision promptly.
If a mistake is found before subordinate issuance, preserve evidence and correct the new design under review. After trust and subordinate certificates exist, reinstalling or deleting the root is not an ordinary rollback. Retain the original identity and follow PKI incident or retirement procedures. The managed outcome is a maintainable hierarchy with an intentionally narrow offline signing function and verifiable public distribution.
 Establishing an AD-integrated root certification authority deliberately
Establish an enterprise root CA only after deciding trust, keys, publication and ownership, then validate separate issuance and revocation…
 Designing an AD CS template with a narrow enrollment boundary
Design a restricted AD CS template as an issuance policy, separate AD creation from CA enablement, validate subject and key controls, and…
 Rolling out certificate auto-enrollment with a measurable pilot
Roll out certificate auto-enrollment through a narrow user or computer pilot, align template and GPO eligibility, inspect issued keys and…
 Enrolling an enterprise certificate for the actual web-service name
Enroll a machine-held enterprise TLS certificate for the real service DNS names, respect template approval and key policy, inspect the…
 Making a certificate revocation reach the relying application
Carry one approved certificate revocation from issuer and serial verification through reason selection, CRL publication, endpoint delivery…
