Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Define what should happen without a person clicking Enroll
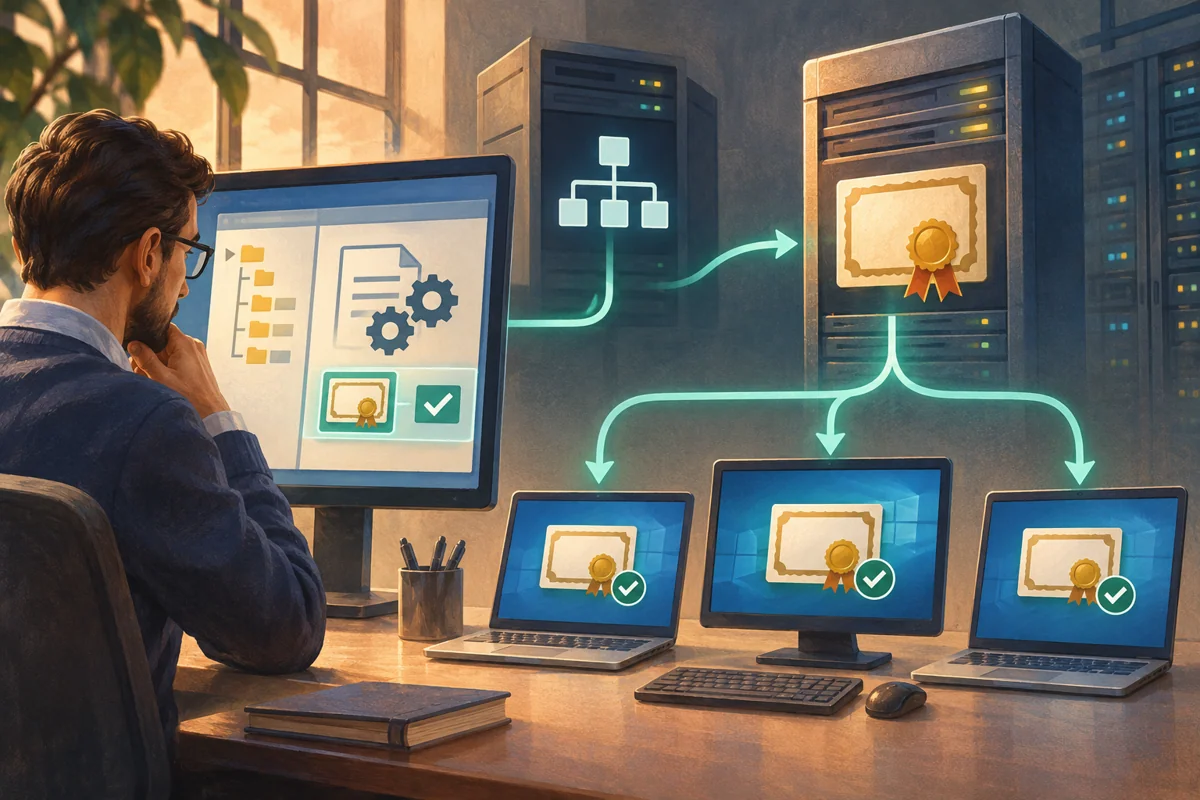
Certificate auto-enrollment lets an eligible user or computer obtain and renew certificates through policy. Its convenience depends on a precise boundary: the correct identity must receive the correct template, store the key in the correct context and renew before the service is affected. Enabling one Group Policy setting does not create that complete workflow.
For managed Netcloud24 environments, the team prepares the templates, policy targeting and service integration. Customers should receive the intended working certificate-backed service rather than have to request certificates manually on every server. This article describes the administrator’s staged rollout and the evidence needed to distinguish successful policy processing from successful application renewal.
Choose user or computer enrollment deliberately
A computer policy acts in the machine context and normally places certificates in the Local Computer store. A user policy acts for the signed-in user and uses their store. A web server, NPS instance or machine-authentication service usually needs a different context from a user signing documents. Applying both policy branches without a requirement can create unnecessary credentials and confuse diagnosis.
Start with a small OU or security-filtered pilot group containing representative systems. Identify operating-system and application support, connectivity to AD and the issuing CA, and the required trust and revocation paths. Non-domain and disconnected devices may need another enrollment method; do not assume ordinary domain GPO reaches them.
Decide how the service discovers and uses a renewed certificate. Auto-enrollment placing a new certificate in a store does not necessarily update an IIS binding, application thumbprint or external appliance. That integration needs its own supported process and acceptance check.
Prepare an auto-enrollable template
Use an approved custom template with the intended purposes, cryptography, identity construction, validity and renewal period. Give the target group Read, Enroll and Autoenroll, and ensure the issuing CA can read the template. Publish it on the intended CA after AD replication. Keep administration permissions separate from enrollment rights.
A template requiring manual approval or input may not complete unattended. Requester-supplied identity, exportable keys or authentication purposes require extra care. For AD certificate authentication, verify current strong identity mapping requirements rather than relying on old weak-name assumptions. Do not broaden enrollment groups to compensate for a policy-targeting error.
# On the issuing CA or approved administration system:
Get-CATemplate
# Inspect the pilot computer's directory placement separately:
Get-ADComputer 'APP-PILOT01' -Properties DistinguishedName |
  Select-Object Name,DistinguishedName
Record template short name and display name, intended group, CA and store context. Those details make a later “certificate missing” incident much more specific than a screenshot of an enabled GPO.
Create the policy in the matching branch
In Group Policy Management, create or edit a dedicated pilot GPO and link it to the reviewed scope. For computer enrollment, open Computer Configuration, Policies, Windows Settings, Security Settings, Public Key Policies, Certificate Services Client – Auto-Enrollment. Configure Enabled and select renewal/update handling and updating certificates based on templates as required by the design.
Use the equivalent User Configuration branch only for the intended user scenario. Review security filtering, inheritance and deny permissions. Do not remove Authenticated Users read access from a policy without preserving the necessary computer read path and understanding current Group Policy processing. Keep scope narrow until the pilot demonstrates both issuance and renewal behaviour.
Document the selected options rather than relying on a generic statement that auto-enrollment is on. Policy determines client behaviour, while template ACL and CA publication determine eligibility. All must agree; no single console page proves the whole chain.
Refresh one pilot and inspect the effective result
On the pilot, refresh the relevant policy and inspect its resultant policy. A forced refresh does not prove enrollment succeeded, and repeated refreshes do not correct a missing template permission. Use the correct account context when requesting an enrollment cycle.
# Computer-policy pilot, from an elevated session:
gpupdate /target:computer /force
gpresult /scope computer /r
certutil -pulse
Get-ChildItem Cert:\LocalMachine\My |
  Select-Object Subject,Thumbprint,NotBefore,NotAfter,HasPrivateKey
For a user pilot, inspect CurrentUser\My and its user policy instead. Verify the new certificate’s template, subject, SAN, purposes, chain and key. A pre-existing unrelated certificate can make a store listing look successful; identify the exact pilot issuance and compare it with the CA request record.
Read client and CA evidence together
Inspect CertificateServicesClient-AutoEnrollment and certificate-enrollment events available on the client, and match their time with the issuing CA’s request disposition. Some relevant channels may need enabling for the planned diagnosis. Preserve the error code and template identity rather than simply restarting Certificate Services.
If policy is absent, investigate link, filtering, inheritance, replication and account placement. If policy applies but the template is not offered, inspect publication, read/enrollment ACLs, compatibility and pending AD changes. If a request is pending, review issuance requirements. If the certificate is issued but the application cannot use it, check store context, private-key access, purposes and service selection.
An expired CRL or unreachable chain location can affect application validation independently of issuance. A successful auto-enrollment event does not prove every relying client trusts the resulting credential. Test from the actual service path.
Prove renewal and replacement before broad rollout
Use a controlled pilot lifecycle to verify renewal timing and the application’s use of the new certificate. Avoid shortening production template validity merely to create a quick test. A representative test template or approved lab can exercise the process without creating unexpected turnover across the fleet.
Check whether renewal reuses or generates a key according to policy and whether service bindings update correctly. If superseding an old template, inspect the behaviour with existing certificates and clients; supersedence is not immediate universal revocation. Retain overlap sufficient for service migration and verify that retired certificates are handled through the approved lifecycle.
Include offline or infrequently connected devices in rollout planning. A renewal window that works for always-connected servers may fail for systems that only occasionally reach the CA. Monitor expiry and failures so the team intervenes before users see a service outage.
Pause safely and retain issued credentials deliberately
If the pilot misbehaves, disable or unlink its GPO scope and stop further template issuance where necessary through a reviewed change. This does not automatically remove or revoke certificates already issued. Decide their disposition separately, especially if a policy issued an inappropriate authentication credential.
Do not delete every certificate in a personal store as cleanup. Identify the exact template and application dependencies first. Preserve logs and CA request records, restore the prior targeting and verify existing services. After acceptance, document policy owner, scope, template, renewal integration and expiry monitoring. The managed result is reliable unattended maintenance with a visible exception path, not merely fewer enrollment clicks.
 Establishing an AD-integrated root certification authority deliberately
Establish an enterprise root CA only after deciding trust, keys, publication and ownership, then validate separate issuance and revocation…
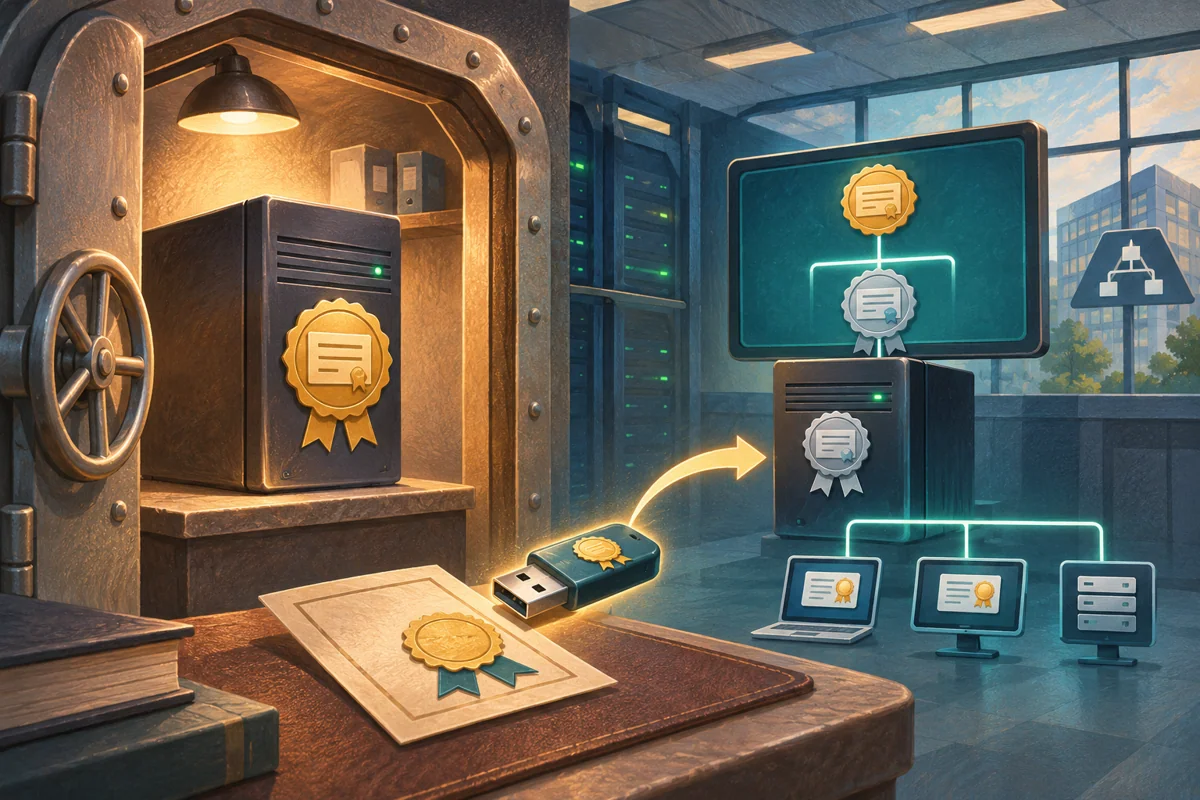 Separating an offline root from day-to-day certificate issuance
Separate offline root signing from enterprise issuance, prepare the standalone trust anchor, review the subordinate request, validate…
 Designing an AD CS template with a narrow enrollment boundary
Design a restricted AD CS template as an issuance policy, separate AD creation from CA enablement, validate subject and key controls, and…
 Enrolling an enterprise certificate for the actual web-service name
Enroll a machine-held enterprise TLS certificate for the real service DNS names, respect template approval and key policy, inspect the…
 Making a certificate revocation reach the relying application
Carry one approved certificate revocation from issuer and serial verification through reason selection, CRL publication, endpoint delivery…
