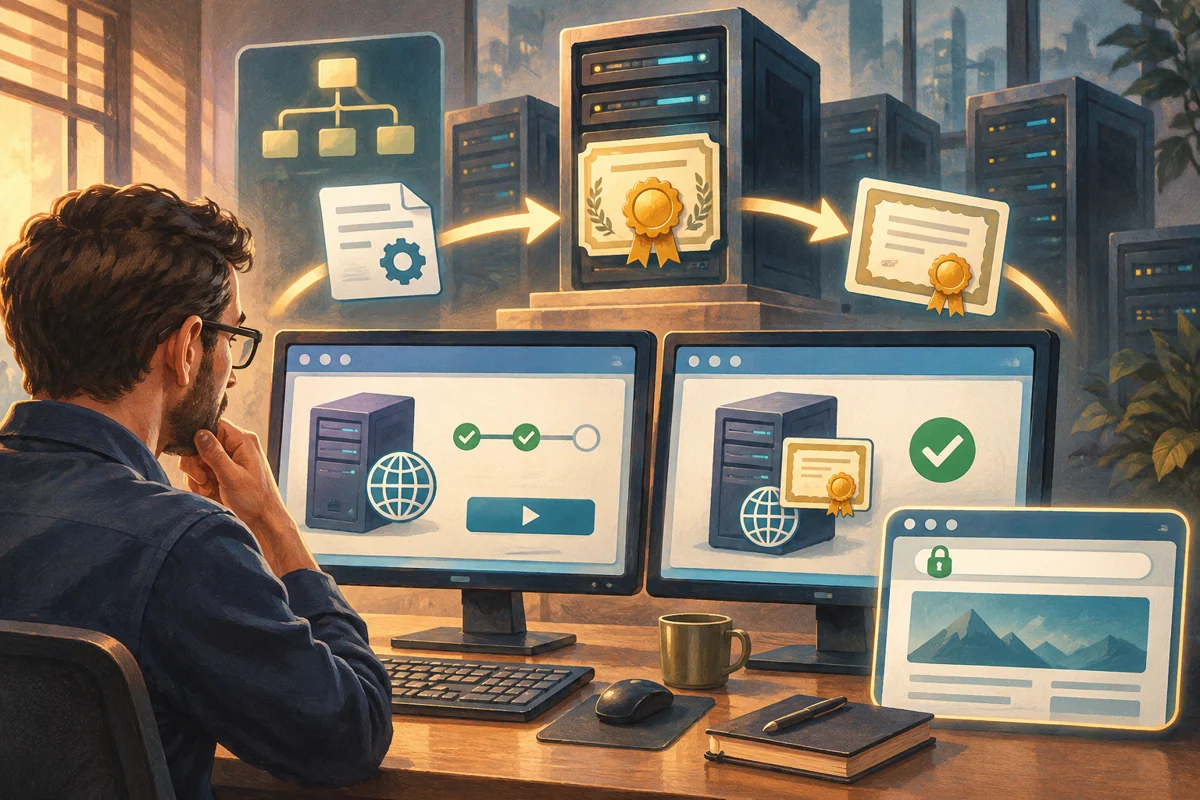
Platform: Windows Server 2019, 2022 and 2025, with the version and hosting restrictions described below.
Start from the name clients will validate
A web certificate identifies the service hostname used by clients, not necessarily the Windows computer that hosts it. A server called WEB-BUILD02 can legitimately serve servicedesk.corp.example, but the certificate must cover that service name and clients must trust its issuer. An enterprise CA certificate is appropriate for a controlled private trust environment; it does not become publicly trusted merely because the website is Internet-reachable.
Within managed Netcloud24 delivery, the team prepares enrollment, private-key handling and the IIS association. Customers receive the working service and renewal expectations rather than a request to approve certificate warnings. This workflow is for an authorised operator enrolling on the machine that will hold the key and verifying the issued result before binding it.
Confirm the template and requesting authority
Identify the approved TLS template, its short name, permitted requester group, purposes and subject rules. If it permits Supply in the request for service DNS names, restrict enrollment and validate those names through the agreed approval process. Do not use a broadly enrollable authentication template with arbitrary subject control as a convenient web-cert workaround.
Check that the template is published by the intended issuing CA and the CA can read it. Confirm compatibility, key-provider support, validity and whether private-key export is permitted. Exportability should follow recovery and deployment policy, not an automatic checkbox. Multiple web nodes may require separate keys or a carefully controlled shared-certificate design.
Use the Local Computer certificate context for the IIS endpoint. A certificate enrolled into the current administrator’s user store can be perfectly valid yet unavailable to the intended service. Keep key generation on the authorised host unless an approved central provisioning process explicitly handles transfer.
Inspect the existing identity and avoid duplicate requests
Open an elevated session and review current machine certificates and bindings. Determine whether this is a first issuance, renewal or replacement after key compromise. Those scenarios can require different key and revocation handling. Do not generate another certificate simply because an existing binding points to the wrong thumbprint.
Get-ChildItem Cert:\LocalMachine\My |
  Select-Object Subject,Thumbprint,NotBefore,NotAfter,HasPrivateKey
Import-Module WebAdministration
Get-WebBinding -Protocol https |
  Select-Object bindingInformation,certificateHash,certificateStoreName
certutil -config - -ping
The CA-selection form of the connectivity check helps identify the available issuer; use the approved CA rather than whichever is selected first. Verify time, DNS and directory connectivity. Preserve existing certificate and key material until its dependencies and replacement policy are known.
Request from the machine enrollment console
Run certlm.msc or open MMC with Certificates for the local computer. Under Personal, start Request New Certificate and choose the approved AD enrollment policy. Select the intended custom web template. If additional information is required, enter the reviewed DNS identities, including the service SAN, using the certificate-properties dialog.
Use only authorised names. A short internal host alias and a public service name can have different validation and ownership requirements. Avoid adding every conceivable alias simply to prevent future requests; each broadens the identity asserted by the key. Confirm the key provider and other request settings match the template and application.
Submit the request and record its outcome. If approval is required, a pending request is expected and should be processed by the designated certificate manager. Do not relax the template’s approval settings globally to accelerate one request. Keep the request identifier and evidence of name authorisation with the service record.
Complete pending issuance without losing the key
Where the request remains pending, obtain the issued certificate from the approved CA process and complete it in the matching machine context. The certificate must be associated with the private key that generated the request. Importing a .cer on a different machine does not create that missing key.
If automated certreq enrollment is used instead of MMC, keep its INF, template attribute and machine-key settings explicit and reviewed. Requester-supplied SAN syntax and policy vary; do not paste a generic request file that enables exportable keys or claims unauthorised names. Use one deliberate enrollment path rather than several overlapping attempts that leave indistinguishable pending keys.
Protect any PFX export with approved encryption, access and secret custody. Do not send private keys or their passwords in ordinary support messages. When a key cannot be exported by policy, use the intended host-specific issuance or key-provider recovery method.
Inspect what the CA actually issued
Check the certificate in Local Computer\Personal and confirm it reports an associated private key. Inspect SAN, subject, Server Authentication purpose, issuer, dates, signature, provider and chain. A template’s desired settings are not a substitute for verifying the actual object.
Get-ChildItem Cert:\LocalMachine\My |
  Select-Object Subject,Thumbprint,NotAfter,HasPrivateKey
# Exported public certificate only, for an approved verification test:
certutil -dump 'C:\PKI-Evidence\ServiceDesk.cer'
certutil -urlfetch -verify 'C:\PKI-Evidence\ServiceDesk.cer'
Use a representative relying client for chain and revocation tests, not only the issuing CA. Verify embedded AIA/CDP retrieval and trust distribution. A successful enrollment proves issuance, while validation shows the client can build and evaluate the chain. Keep those results separate in acceptance evidence.
Associate it with the application through a controlled change
Bind the approved thumbprint to the exact IIS hostname and port using the intended SNI or IP-based model. Preserve the former association and certificate while validating the new endpoint. Test with the service hostname from a real client so certificate-name validation and SNI follow the production path.
Do not bypass trust warnings to call the rollout successful. Check the returned application content too: a valid certificate from the wrong site is still a binding fault. If TLS terminates at a proxy, verify that public endpoint and the proxy-to-IIS leg independently. Enrollment does not automatically configure either association or update a hard-coded application thumbprint.
Make renewal and incident recovery part of handover
Document issuer, template short name, authorised names, key location, binding owner and expiry monitoring. Test how renewal updates the service before the deadline. A replacement certificate in the store does not guarantee the application selects it. Retain overlapping valid identities only for the approved transition period.
For an incorrect name or purpose, stop rollout and request a corrected certificate through policy. For a compromised key, generate a new protected key and follow incident revocation rather than reusing it. Revocation, binding removal and certificate deletion are separate actions. Preserve the service’s working path while resolving the exact fault, and keep customer-facing handover focused on a valid managed endpoint and its support route.
 Establishing an AD-integrated root certification authority deliberately
Establish an enterprise root CA only after deciding trust, keys, publication and ownership, then validate separate issuance and revocation…
 Separating an offline root from day-to-day certificate issuance
Separate offline root signing from enterprise issuance, prepare the standalone trust anchor, review the subordinate request, validate…
 Designing an AD CS template with a narrow enrollment boundary
Design a restricted AD CS template as an issuance policy, separate AD creation from CA enablement, validate subject and key controls, and…
 Rolling out certificate auto-enrollment with a measurable pilot
Roll out certificate auto-enrollment through a narrow user or computer pilot, align template and GPO eligibility, inspect issued keys and…
 Making a certificate revocation reach the relying application
Carry one approved certificate revocation from issuer and serial verification through reason selection, CRL publication, endpoint delivery…
